Author: l0cknsec

  • Trump’s 7 Pressure Points on Korea — How ‘We’ll Remember’ Rewrote the Next 30 Days of the US-Korea Alliance

    Trump’s 7 Pressure Points on Korea — How ‘We’ll Remember’ Rewrote the Next 30 Days of the US-Korea Alliance

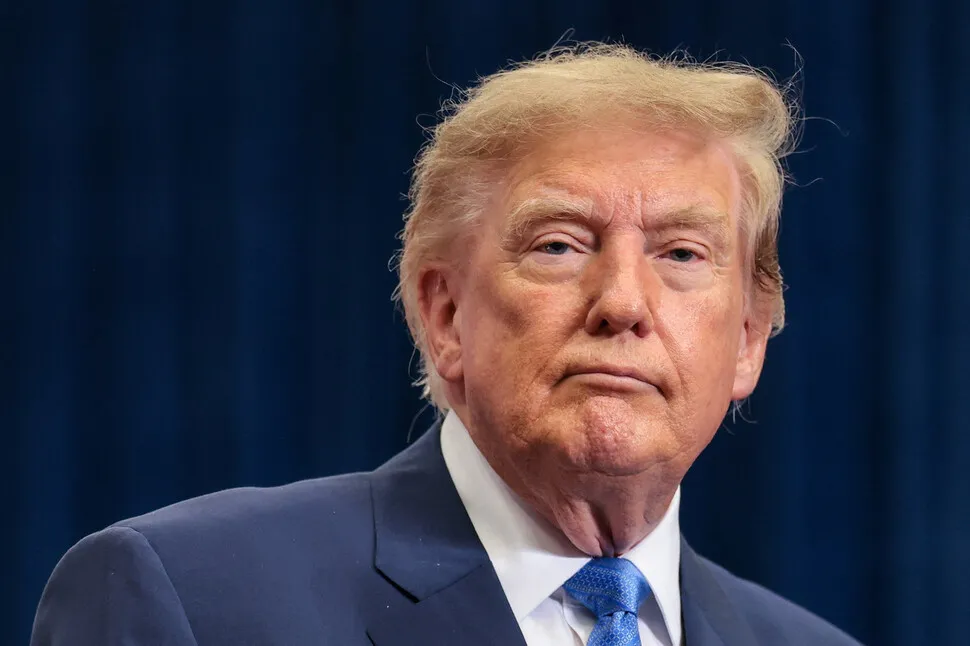
    Trump's Pressure on Korea

    Key Summary

    • President Trump publicly stated in an interview that Korea refused a US request for cooperation regarding Iran, reportedly using the firm expression “we’ll remember that.”
    • The remarks, made during a broadcast interview coinciding with the US political calendar, have been edited and amplified by conservative outlets such as Fox News under the framing of “Korea and NATO security free-riding.”
    • Major Korean media outlets including the Hankyoreh, JoongAng Ilbo, Yonhap News, MoneyToday, and Munhwa Ilbo have provided simultaneous coverage, focusing on the context of the remarks, the Foreign Ministry’s response, and the potential ripple effects.

    Analysis

    Trump’s pressure on Korea has once again surfaced on a public channel — this time triggered by a single interview. He confirmed that “Korea refused a US cooperation request regarding Iran” and added, “we’ll remember that.” That single line reads less like an emotional outburst and more like a deliberate pressure to rewrite the price tag of US-Korea security cooperation.

    The Hankyoreh and JoongAng Ilbo reported that Fox News, a US conservative outlet, edited and amplified the remarks under the framing of “Korea and NATO security free-riding.” The Korean Foreign Ministry issued an official comment without delay, while the National Assembly and expert groups called for a consistent response strategy.

    Issue 1. The Facts Behind the Remarks — How Much of the Iran Cooperation Refusal Is True?

    No specific details have been released about the type of cooperation the US requested from Korea. JoongAng Ilbo reported the explanation from a senior Korean government official alongside the US position, stressing that fact-checking must come first. The core message of the Yonhap News summary of the Foreign Ministry’s comment focuses on “reaffirming the current state of US-Korea security cooperation.”

    From a practitioner’s perspective, what stands out is that the scope of the cooperation request (command-level intelligence sharing, safety of round-trip shipping routes, deployment of non-combat assets, etc.) and the reasons for refusal remain unclear. This vacuum is highly likely to be filled by the US “free-riding” framing going forward.

    Issue 2. The Evolution of the ‘Security Free-Riding’ Frame

    According to Munhwa Ilbo’s analysis, Fox News’ coverage of Korea functions not as simple reporting but as a strategic rhetoric targeting the Korean Peninsula. The “security free-riding” expression was repeated during the first Trump administration, but this time it carries different weight because it is tied to the practical interests of tariff negotiations.

    Republican hardliners are moving to link this framing to a hike in SMA (Stationing of US Forces Korea) cost-sharing and higher tariffs on Korean automobiles and steel. Meanwhile, traditional diplomatic experts remain skeptical about coupling the Iran-Middle East issue directly with US-Korea security. A recent column on why US-Korea alliance trust is being shaken again also highlighted the recurrence of the same fracture pattern.

    Issue 3. US-Korea Tariff Negotiations — The Variable Created by Trump’s Pressure on Korea

    MoneyToday analyzed that Trump’s latest pressure on Korea will directly affect tariff negotiation variables. The likelihood that SMA and tariff negotiations will be bundled into a single package — rather than handled on separate tracks — has grown significantly.

    From Korea’s perspective, its negotiation leverage could weaken. If the “security free-riding” frame gains legitimacy in the US Congress and public opinion, Korea will face the burden of not simply “paying more” but of demonstrating “what it contributes and how.”

    Issue 4. North Korea Policy Coordination — The Iran-Ukraine-North Korea Connection

    A structure in which Korea’s Middle East policy produces a counterproductive effect on Korean Peninsula security has come into view. If Korea remains passive on Iran sanctions coordination, it opens the door to expanded interpretations regarding its willingness to support Ukraine or participate in North Korea sanctions. US hardliners are applying a “linked alliance” test that places these three axes on equal footing.

    Issue 5. The Korean Government’s Response Options Matrix

    In the short term, it is critical not to stop at surface-level explanations. The options, organized along a timeline, are as follows.

    • Short term (1–2 weeks): Alongside a Foreign Ministry-level fact-check, explicitly enumerate the areas where Korea can contribute within the Iran-Middle East cooperation scope (e.g., non-combat support for escort operations, humanitarian aid).
    • Medium term (1–3 months): Time the presentation of a security contribution package (joint training participation, expanded combined exercises, advanced technology cooperation) to coincide with the resumption of SMA negotiations.
    • Long term (1 year): Build an independent diplomatic line to create a diplomatic portfolio with broader options between the US, China, and Japan.

    The author views this as the most meaningful point. If it ends with a short-term explanation, the “we’ll remember” remark will reappear as the next negotiation card, but if a security contribution package follows, it could instead become an opportunity to redefine the alliance.

    Issue 6. Scenario Analysis — Three Paths After Trump’s Pressure on Korea

    The baseline scenario is managed by both sides. The US adjusts the intensity of its remarks while shifting pressure to the SMA negotiation table, and Korea patches the fracture with an additional contribution proposal. This is the most likely path.

    The risk scenario occurs if the framing by the US Congress and conservative media becomes entrenched, with tariffs and cost-sharing presented as a single bundle. This opens the door to sector-specific tariff strikes on Korean automobiles and semiconductors.

    The opportunity scenario points in an unexpected direction. If Korea presents a “comprehensive security contribution roadmap” linking Iran-Middle East-North Korea, it could become an opportunity to redefine the US-Korea alliance from a cost-sharing arrangement to a value-based partnership. Follow-up reporting by the Hankyoreh also hints at this direction.

    Issue 7. Monitoring Checkpoints for the Next 30 Days

    The five immediate checkpoints for practitioners are as follows.

    • Korea’s Foreign Ministry follow-up official position (within 1 week)
    • US Department of Defense and National Security Council (NSC) briefing content (1–2 weeks)
    • Announcement of the next SMA meeting schedule (within 2 weeks)
    • Timing of Korea’s announcement of additional Iran-Middle East measures (2–3 weeks)
    • Tone of US congressional hearings and follow-up coverage by Fox and other conservative media (ongoing)

    Conclusion — Read It as a Request to Reset the Price Tag

    The essence of Trump’s pressure on Korea is not emotion but a price tag. The signal should be read as a renewed question about what contributions and roles Korea should take on — not just viewing the cost of the US-Korea alliance in monetary terms alone. If Korea stops at short-term explanations, the “free-riding” framing will become entrenched, but if it puts forward a package-type proposal, its negotiation leverage can actually come alive. The next 30 days are likely to be the turning point.

    Summary of Issues

    • Facts of the remarks: The lack of specificity in the US request creates a vacuum that will be filled by future framing.
    • The ‘security free-riding’ frame: Its weight has shifted from rhetoric to a negotiation card.
    • Tariff-SMA linkage: Security issues are being directly connected to the trade track.
    • North Korea coordination: The Iran-Ukraine-North Korea linkage test has begun.
    • Response options: A medium- to long-term contribution package preserves negotiation leverage better than a short-term explanation.

    What to Do Right Now

    • Check the Foreign Ministry’s official comments and follow-up positions weekly and organize them on a timeline.
    • Verify Korea’s current status regarding Iran-related exports and sanctions participation using data from the Korea International Trade Association and the Korea Customs Service.
    • Track US congressional hearing schedules and coverage by Fox, WSJ, and other conservative outlets via RSS.
    • Obtain the latest industry and outlook reports on SMA negotiations (KDI, KIEP).
    • Set up internal KPIs for the share of Korean exports to the US by sector, including automobiles and semiconductors.

    Frequently Asked Questions

    What exactly did Trump say regarding pressure on Korea?

    During a broadcast interview, Trump publicly stated that Korea refused a US request for cooperation regarding Iran, adding “we’ll remember that.” The US side has not disclosed the specific details of the request.

    Why is the ‘security free-riding’ frame resurging?

    Conservative outlets such as Fox News have been editing their coverage to bundle US-Korea alliance cost-sharing and tariff negotiations together, shifting the weight from simple rhetoric to a negotiation card. This is reinforced by Republican hardliners’ demands to link SMA and tariffs.

    How far has the Korean government’s response progressed?

    The Foreign Ministry issued an official comment reaffirming the current state of US-Korea security cooperation. However, if it stops at a short-term explanation, the US “free-riding” framing could become entrenched, and the formulation of a medium- to long-term contribution package is being raised as the next move.

    What is the most important variable in the next 30 days?

    The next SMA meeting schedule and the timing of Korea’s announcement of additional Iran-Middle East measures. The content of US Department of Defense and NSC briefings, along with the tone of US congressional hearings, must be monitored simultaneously.
  • 5 Lessons from the Berlin Ransomware Attack — What the Rhysida Breach Means for Public Institutions

    5 Lessons from the Berlin Ransomware Attack — What the Rhysida Breach Means for Public Institutions

    Berlin Ransomware

    Key Summary

    • The Berlin city government officially confirmed that the Rhysida ransomware gang posted a confession on a dark web leak site and is now attempting financial extortion against the city
    • Attackers gained initial access weeks before being detected and performed lateral movement across parts of Berlin’s administrative network, according to the investigation
    • Exposed data is believed to include personnel records, citizen service information, and internal financial records; the full scope of the breach remains under forensic investigation

    Analysis

    The Berlin ransomware incident is not just a simple hacking case. The Berlin city government officially confirmed that the Rhysida gang posted a confession on a dark web leak site and is now attempting financial extortion. Weeks before detection, the attackers had already completed lateral movement across sections of Berlin’s administrative network.

    This is the most painful point from a practitioner’s perspective. The fact that a city-scale administrative network failed to detect external intruders for weeks means that internal visibility and anomaly detection systems were not properly in place.

    Berlin Ransomware Breach Timeline — From Initial Access to Data Exfiltration

    According to the Berlin city government’s announcement, the attack followed a typical ransomware intrusion pattern. Initial entry is believed to have come through phishing emails, exposed VPN/RDP endpoints, or external Initial Access Brokers (IABs). This was followed by a double-extortion tactic: abusing legitimate cloud services (remote management tools, file sharing) to exfiltrate data, and then deploying bulk encryption at the end.

    According to BleepingComputer’s report, the leak site is believed to include personnel records, citizen service information, and internal financial records. The exact scope of the breach will be confirmed by the forensic investigation at Berlin’s IT Coordination Office (ITDZ Berlin).

    The Rhysida Gang’s RaaS Structure and Tactics

    Rhysida is a Ransomware-as-a-Service (RaaS) operation that first appeared in 2023. Core operators provide the ransomware builder and leak site infrastructure, while affiliate attackers use these tools to perform their own intrusions. The profit split between attackers and operators is typically known to be around 7:3 to 8:2.

    Rhysida’s weapon is its consistent target selection across healthcare, government, education, and manufacturing sectors. Ransoms are typically set in the seven-figure dollar range, and if unpaid, the leaked data is released in stages to apply pressure. The fact that the Berlin ransomware incident followed the same pattern confirms that the gang’s operational playbook works just as well against public institutions.

    Primary and Secondary Damage Scenarios

    Exposed personnel and financial data immediately becomes phishing fodder. An attacker who knows employee names and internal report titles can craft a convincing email disguised as a “security check notice.” Under GDPR, the city of Berlin has notified the relevant supervisory authority of the breach, but the real danger concentrates in the days immediately following notification. This is because secondary phishing attacks, crafted from the externally exposed information, will target both city employees and citizens at the same time.

    What I consider the most serious aspect of this incident is the length of the compromise period. The fact that lateral movement was possible for weeks strongly suggests that the attacker obtained domain controller privileges.

    Incident Response — ITDZ Berlin’s 7-Day Sprint

    The city of Berlin is simultaneously working with external incident response teams on the following tasks: blocking intrusion paths, bulk revoking compromised credentials, auditing access paths, and collecting forensic evidence. The city’s data protection authority is gradually disclosing the scope of the exposed information to citizens.

    The GDPR notification obligation is 72 hours, but full response completion can take several months. Looking at similar European public institution cases, some have taken 4 to 6 months just to recover their administrative networks.

    5 Lessons from the Berlin Ransomware Incident for Public Institutions

    The Berlin ransomware case vividly demonstrates what risks city-scale infrastructure faces. Compared to U.S. city government breach cases, the initial intrusion vectors are strikingly identical: unpatched VPN/RDP gateways, reused service account passwords, and SIEMs with anomaly alerts turned off.

    In a similar context, as seen in the article China Hacking Correction: Words Reversed in Just 3 Days, cyberattack incidents often see the truth shift during the post-incident reporting process. The final damage scale of the Berlin ransomware case could also vary significantly based on forensic investigation results.

    Key Issues

    The Berlin ransomware incident raises three core issues.

    First, weeks of detection failure exposes the limitations of public institution SIEMs. Second, VPN/RDP patching cycles are slower than attackers’. Third, double extortion must now be assumed as the baseline scenario for public institutions.

    What to Do Right Now

    • Extract the list of externally exposed VPN/RDP gateways today and compare them against patched versions
    • Audit whether administrator account passwords are being reused and immediately rotate domain controller credentials
    • Verify that SIEM anomaly detection rules are enabled and add Indicators of Compromise (IoC) feed sources
    • Verify that backup data is stored separately in offline, immutable storage
    • Run at least one secondary phishing simulation drill for employees within this week

    Frequently Asked Questions

    What is Rhysida ransomware?

    It is a RaaS-type ransomware gang that appeared in 2023, primarily active in healthcare, government, and education sectors. It mainly uses double-extortion tactics, and ransoms are typically set in the seven-figure dollar range.

    Did the Berlin city government pay the ransom?

    The Berlin city government’s official position is refusal to negotiate. In general, public institutions have a strong tendency to decide not to pay ransoms.

    How is the leaked citizen information being protected?

    Berlin’s data protection authority is currently analyzing the scope of the leak, and citizens will be notified in stages. Under GDPR, the supervisory authority was notified within 72 hours.

    Could the same thing happen to Korean public institutions?

    Yes, the same initial intrusion vectors exist in Korea. VPN patch delays and credential reuse are common issues across global public institutions.

    The Berlin ransomware case ultimately demonstrates the structural vulnerabilities of public sector cybersecurity. The scarier fact isn’t the intrusion itself, but that it went undetected for weeks. Even after the external incident response team completes intrusion blocking and credential revocation, the secondary phishing risk will persist for at least a quarter. Operations teams must keep this in mind.

  • Three Core Issues in EU DSA Regulation — What the ChatGPT and Reddit VLOP Designations Really Mean

    Three Core Issues in EU DSA Regulation — What the ChatGPT and Reddit VLOP Designations Really Mean

    EU DSA regulation

    Key Summary

    • The European Commission and Digital Services Act (DSA) supervisory authorities have officially designated OpenAI’s ChatGPT and Reddit as “Very Large Online Platforms (VLOPs),” the top tier based on user count.
    • Effective immediately, both services must carry out enhanced obligations across the EU, including risk assessments, publication of transparency reports, public disclosure of illegal-content response systems, granting data access to external researchers, and strengthened measures for child protection and cyberbullying prevention.
    • As a generative AI service, ChatGPT must submit a dedicated risk assessment covering harms from hallucinations, deepfakes, and harmful content for minors. Reddit must demonstrate that its community self-governance structure (Mod/Subreddit) satisfies the DSA’s “systemic risk” requirements.

    issues

    EU DSA regulation drew a new benchmark at the end of August. The European Commission has designated OpenAI’s ChatGPT and Reddit as “Very Large Online Platforms (VLOPs),” the top tier based on user count. Effective immediately, both services must fulfill enhanced obligations, including risk assessments, transparency reports, external researcher data access, and child protection systems.

    ChatGPT is the first generative AI service to be included as a VLOP. Reddit is the second U.S.-origin UGC platform after X to receive the designation. I see the two designations as sending different signals. One is the fact that “AI services are now subject to platform regulation,” and the other is a new test of whether “community self-governance will be recognized by regulators.”

    1. A Separate Risk Assessment for Generative AI — Hallucinations and Minor Protection

    The risk assessment ChatGPT must submit differs in character from that of a typical VLOP. EU DSA regulation classifies the risks arising from generative AI’s “synthetic content” as a separate category. From misinformation caused by hallucinations, to harmful responses to minors, to the potential abuse of image-generation features for deepfakes — OpenAI must document its mitigation measures and incident-response systems for each of these items.

    The reason this is practically difficult is that the outputs of large language models are non-deterministic, so traditional “content moderation checklist” approaches cannot fully control the risk. As a result, OpenAI is likely to submit its own documents, such as model cards and system cards, together with user feedback loops and safety-classifier performance metrics. How far EU regulators require that data to be disclosed to external researchers will be a key variable going forward.

    2. UGC Platforms’ Self-Governance Structure — Reddit’s Systemic Risk Proof

    Reddit’s designation poses a different test. The DSA requires VLOPs to conduct a “systemic risk” assessment. The scope covers the spread of illegal content, impact on elections and public health, child protection, gender-based violence, and cyberbullying.

    Reddit’s self-governance structure — its moderators and Subreddit operators — has long functioned as the backbone of content moderation. But EU DSA requirements are not satisfied merely by the fact that a structure exists. The EU requires proof that (1) policies are actually enforced, (2) moderators are given adequate tools and training, and (3) platform-level escalation paths function when inappropriate content arises. In other words, for self-governance to be recognized as “systemic safety,” performance metrics for that self-governance are needed. The metrics Reddit puts forward will be an industry-wide focal point.

    3. Transparency Reports and External Researcher Data Access

    The two most contentious provisions in the DSA are the biannual transparency reports and data access for “vetted researchers.” OpenAI must decide how to handle areas that directly collide with trade secrets, such as model weights, training data, and prompt logs. Reddit must determine how much information about deleted posts, locked subreddits, and banned users it will expose to researchers.

    The interesting part is that both companies have already been effectively treating EU DSA regulation as a de facto global standard. Google, Meta, and X applied DSA standards to their global operations from the first round of VLOP designations in 2024. This latest inclusion is the next chapter in that trend, and once rules are set, they effectively spread as the same UX to users outside the EU — the so-called “Brussels Effect.” It is worth watching how future EU DSA regulation technical standardization work expands into the global supply chain and researcher ecosystem.

    Global Ripple Effects — Where the U.S., U.K., and Korea Stand

    The Brussels Effect of EU DSA regulation is already in motion. The United States continues to push the Kids Online Safety Act (KOSA) at the federal level in 2024. The United Kingdom has already entered the first implementation phase under its Online Safety Act. South Korea is also moving in the same direction through revisions to its Child and Youth Protection Act and discussions on a basic AI law.

    Nonetheless, there are differences in pace and texture. The EU groups “platforms” as a unit and demands governance, transparency, and researcher access all at once. In contrast, the U.S. has fragmented federal and state laws, and the U.K. applies tiered rules by media type. South Korea’s basic AI law is likely to be designed around “impact assessment,” giving it a more industry-friendly tone than the EU DSA. Even so, one fact remains the same — any service that does not follow the EU DSA regulation benchmark loses the EU market.

    Key Issues at a Glance

    There are three issues this designation highlights.

    • Generative AI is classified separately as a “synthetic content” risk, and model cards and safety-classifier performance effectively become regulatory reports.
    • A community self-governance structure is not sufficient on its own; enforcement metrics, escalation paths, and moderator tools must be demonstrated together.
    • Transparency reports and researcher data access directly conflict with trade secrets, so consent procedures, ethics review, and publication guidelines must be designed in advance.

    What to Do Right Now

    • Check the European Commission’s VLOP list and simulate whether your service will reach the threshold (45 million monthly EU users) within the next 12 months.
    • Draft a vetted researcher collaboration guideline, including data scope, consent procedures, and publication requirements.
    • Build a data pipeline that can automatically aggregate the 11 transparency items required by the DSA on a biannual basis.
    • Consolidate safety-classifier, content-moderation, and ad-library data into a single dashboard and standardize quarterly compliance reviews.
    • Set up a translation pipeline that can simultaneously deliver transparency reports, terms of service, and safety guides in English, German, and French.

    Frequently Asked Questions

    Is VLOP designation mandatory?

    Yes, it is mandatory. Once the European Commission determines that the user-count threshold is met, it designates the service, and the designation cannot be refused. Violations can result in fines of up to 6% of global revenue.

    Does the ChatGPT designation apply to all of OpenAI?

    No. The designation applies to the ChatGPT service itself. OpenAI’s API business and other models are separate, although safety measures equivalent to those for a VLOP are likely to be indirectly required for services accessed via the API.

    Why was Reddit designated later than X?

    The EU only counts EU residents and excludes non-logged-in visits and API calls. Reddit’s share of EU users is analyzed to have been lower than X’s, which is considered a factor in the delay.

    Can a Korean business ignore EU DSA regulation?

    It would face service blocking in the EU. Since 2024, equivalent safety laws have been introduced in succession in the U.S., Korea, and Japan, making it a de facto global standard. A detailed analysis is available in Four Issues in the First Application of EU AI Regulation.

    This article was prepared based on Ars Technica’s reporting on the VLOP designations. Further English analysis can be found in The Standards Competition Created by ChatGPT’s VLOSE Designation.

  • EU AI Regulation: 4 Key Issues in Its First Application — The Standards Race Triggered by ChatGPT’s VLOSE Designation

    EU AI Regulation: 4 Key Issues in Its First Application — The Standards Race Triggered by ChatGPT’s VLOSE Designation

    Key Summary

    • OpenAI’s ChatGPT has been officially classified as a ‘Very Large Online Search Engine (VLOSE)’ under the EU Digital Services Act (DSA)
    • The DSA mandates systemic risk assessments, transparency reporting, and independent audits for very large platforms and search engines with 45 million or more monthly active users in the EU
    • OpenAI must demonstrate concrete mitigation measures across four areas: ① Minor protection (strengthening safety guardrails against self-harm and suicidal ideation), ② Mental health (detecting and intervening in dependency or psychologically harmful conversation patterns), ③ Illegal content blocking (child sexual abuse material, terrorist content, and intellectual property infringement), and ④ Algorithmic transparency (evaluating the impact of recommendations and model updates and disclosing them to EU users)

    Policy Analysis – An insight column diagnosing the structural impact of the EU’s first generative AI regulation case on global AI industry governance and summarizing the issues the industry must address

    The EU AI regulation has been applied to a generative AI service for the first time. OpenAI’s ChatGPT has been officially classified as a ‘Very Large Online Search Engine (VLOSE)’ under the EU Digital Services Act (DSA). Having surpassed the 45 million monthly active user threshold, and given that users directly leverage model outputs in the form of search, summary, and recommendations, its influence comparable to that of a search engine has been recognized.

    This classification is not mere labeling. Three obligations—systemic risk assessment, transparency report submission, and external independent audit—fall squarely on OpenAI. Although the DSA took effect in August 2024, this is the first time a generative AI service has been designated as a VLOSE. Until now, only Google Search, Microsoft Bing, and Yahoo had held that VLOSE designation.

    What I find noteworthy at this juncture is the ‘expansion of definition.’ The fact that the interpretation including ‘conversational AI responses’ within the search engine category has been formalized. This precedent effectively sets the baseline for the next EU AI regulation case.

    Four Key Areas OpenAI Must Demonstrate

    The European Commission has required concrete mitigation in four areas. First, minor protection. OpenAI must demonstrate that guardrails actively block output patterns that encourage self-harm and suicidal ideation. Second, mental health. Procedures must be in place to detect and intervene in signals that a given user is over-relying on the chatbot—the so-called ‘psychologically harmful conversation patterns.’

    Third, illegal content blocking. A filtering system is required to ensure that child sexual abuse material, terrorism-related content, and intellectual property-infringing content are neither generated nor disseminated. Fourth, algorithmic transparency. The impact of recommendation logic and model updates on output results must be assessed and disclosed to EU users.

    Among these four, the most demanding is the transparency report. This does not mean revealing model weights or training data themselves. However, changes must be documented in a traceable form, showing ‘what was changed and what user impact that change produced.’ Because this is an area where OpenAI has historically preferred non-disclosure, practical conflicts are inevitable. The core of the EU AI regulation lies in this transparency reporting.

    The Enforcement Weapon: 6% of Global Revenue

    The European Commission can issue formal information requests to OpenAI and, if necessary, conduct on-site inspections. If a DSA violation is confirmed, fines of up to 6% of global revenue can be imposed. Based on OpenAI’s approximately $3.7 billion in revenue as of 2024, even a simple calculation yields an enormous amount. Indeed, the DSA fines already imposed on Google and Meta have run into the billions of euros.

    The scenario most discussed in the industry is ‘EU market functionality reduction.’ This is because regulatory avoidance is possible by disabling certain model updates or new features for EU users only. Meta has, in fact, made similar choices regarding its News tab features. This is the backdrop for speculation that a ‘EU-only lite version’ of generative AI services could emerge.

    Spillover to Competing Models and Global Ripples

    The ripple effects of this EU AI regulation application extend beyond OpenAI. Google Gemini, Anthropic Claude, and xAI Grok also stand before the same logic. Any service with more than 45 million EU users cannot escape VLOSE classification. Considering the ongoing trend of Google Search integrating with Gemini, Gemini’s VLOSE designation is only a matter of time.

    Other jurisdictions—Brazil, the UK, and Korea—are also highly likely to adopt the EU AI regulation case as a de facto reference standard. With the EU AI Act simultaneously advancing its regulation of high-risk AI systems, generative AI providers must bear a dual regulatory framework of the DSA and the AI Act. This creates a pace of EU AI regulatory standardization distinct from markets like the United States and China, which move under single federal regulation.

    From a practitioner’s perspective, what stands out is that the competition over regulatory standards has been re-ignited on top of the aging category of ‘search engine.’ In an era where AI generates information, regulatory authorities across countries have entered a full-scale tug-of-war over how to define the ‘intermediary of information.’ Governance discussions at the data infrastructure level have already been addressed in the Semantic Architecture: 3 Core Axes Analysis.

    This EU AI regulation decision has effectively become the starting point of a global de facto standard. Subsequent jurisdictions are likely to copy this case wholesale, and every AI provider considering entry into the EU market must pass this benchmark. The EU AI regulation standard is highly likely to solidify as the benchmark. Further details can be verified in The Verge’s report on OpenAI ChatGPT and the EU DSA.

    What to Do Right Now

    • Audit the monthly active user count of your EU-targeted services in the 44.5–45 million range and simulate when you might cross the VLOSE threshold.
    • Establish an internal logging system that automatically records model update history alongside user impact assessment items.
    • Draft 10 risk scenarios related to minors and mental health, and document blocking and intervention procedures for each.
    • Build a legal and compliance hotline capable of responding to European Commission information requests within 72 hours.
    • Institutionalize a quarterly governance meeting where technology, legal, and product teams jointly review plans to limit features in the EU market.

    Key Issues Summary

    • Definition Debate: The European Commission’s interpretation of whether AI responses fall within the scope of ‘search engine’ will set the baseline for all future generative AI regulation.
    • Dual Burden: DSA VLOSE obligations and EU AI Act high-risk AI obligations apply simultaneously to the same provider, potentially increasing compliance costs geometrically rather than linearly.
    • Market Fragmentation: An EU-only reduced version—the ‘regulatory dark age’ strategy—is likely to become a new global SaaS standard.
    • Standards Race: If subsequent regulators in Brazil, the UK, and Korea effectively adopt the EU case as their benchmark, a global de facto EU AI regulation standard will solidify.

    Frequently Asked Questions

    What is a VLOSE?

    A Very Large Online Search Engine as defined by the DSA, referring to services with more than 45 million monthly active users in the EU. Once designated, systemic risk assessment, transparency reporting, and external audits become mandatory.

    Why was ChatGPT classified as a search engine?

    The pattern of users directly leveraging ChatGPT’s responses for information search, summary, and recommendation has grown, and the user base exceeded the DSA threshold. The European Commission deemed this comparable to search engine functionality.

    What is the maximum fine that can be imposed on OpenAI?

    If a DSA violation is confirmed, up to 6% of global revenue can be imposed. Even based on OpenAI’s approximately $3.7 billion in 2024 revenue, this would amount to a massive sum.

    Will Google Gemini and Anthropic Claude face the same regulation?

    If their EU user base exceeds the threshold, they will face the same VLOSE regulation. Given the trend of Gemini integrating with Google Search, its designation is highly likely.