
Key Takeaways
- Following the financial sector, two major South Korean churches have been exposed to cyberattacks, with approximately 1 million congregant personal records and offering details confirmed to have been leaked. The incident shows that religious institutions are emerging as the new primary targets of cyberattacks.
- While tracking suspected hacking IPs, Oasis Security discovered a large overseas attacker server containing data believed to have been exfiltrated in August from the integrated information systems and groupware of Seoul’s Yeouido Full Gospel Church and Seocho-gu’s Sarang Church.
- Analysis shows that Yeouido Full Gospel Church’s servers were breached via a web shell, through which attackers obtained ERP database administrator privileges, exfiltrating 47.3GB of data in total: 960,000 updated congregant records from the past two years, 330,000 offering-related entries, and 68,000 electronic approval documents.
Religious and nonprofit organizations, which have traditionally not been primary targets of cyberattacks, have effectively become prime targets in their own right, holding data assets on par with financial and public institutions within their integrated ERP and groupware environments. The classic intrusion paths of web shells and pre-stolen credentials, combined with AI agent-driven automated attacks, are lowering the cost of this target expansion and driving up attack success rates.
Table of Contents
- Key Takeaways
- Why Are Churches the Next Stage After the Financial Sector?
- Yeouido Full Gospel Church Intrusion Path: From Web Shell to ERP Admin Privileges
- Sarang Church Intrusion Path: Pre-Stolen Credentials and the SSO Trap
- AI Agents Automated the Attack Documentation
- Second-Stage Damage Scenarios: Smishing and Phishing Armed with Leaked Data
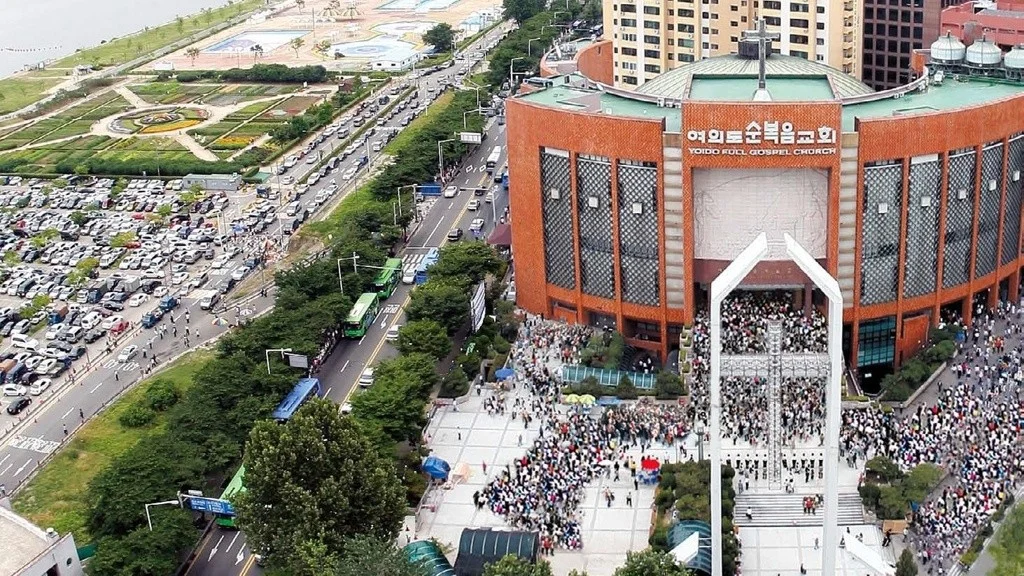
Before the shock of financial-sector breaches has even faded, church hacking is now in the crosshairs. In August, the integrated information systems of Seoul’s Yeouido Full Gospel Church and Seocho-gu’s Sarang Church were breached in quick succession. The Korea Internet & Security Agency (KISA) traced 47.3GB of data believed to have been exfiltrated from the two churches to an overseas attacker server, and the findings were publicized through a Boan News report. Personal information on close to 1 million congregants, along with offering and electronic approval documents, was siphoned out in a single sweep. This is no ordinary data breach. It is a signal that religious institutions have become primary targets of cyberattacks.
Why Are Churches the Next Stage After the Financial Sector?
Across enterprise incident response investigations, attackers systematically prioritize the path of least resistance. Religious institutions are operated primarily around worship and missions, so their security staffing and budgets are often shockingly thin compared with public and financial institutions. And yet inside they run ERP, groupware, electronic approval, offering management, and congregant DBs, all tightly integrated. On the surface they are nonprofit, but the density of their data assets is no different from that of financial institutions. As shown in recent AI-driven breach analyses targeting the financial sector, attackers are already shifting the stage toward “cost-effective targets.” Religious institutions were the next candidates on that list.
Yeouido Full Gospel Church Intrusion Path: From Web Shell to ERP Admin Privileges
Looking at the Yeouido Full Gospel Church case, the attacker got their first foothold through a web shell. A web shell is a small script uploaded to a vulnerable web application to enable remote command execution, typically containing functions such as eval, base64_decode, system, and passthru. In this incident, the web shell was used to infiltrate the server and then obtain administrator privileges on the Enterprise Resource Planning (ERP) database. As a result, 960,000 congregant records updated over the past two years, 330,000 offering records, and 68,000 electronic approval documents were all exfiltrated at once.
Why did this happen? Most web shell intrusions are difficult to block with a single WAF rule. Attackers interleave file upload requests within normal traffic, and once a file is uploaded, they split their commands across multiple calls. The most commonly missed trap in the field is the change in file size of 200 OK responses logged in IIS and Apache access logs. If you miss patterns in which a normal image file suddenly drops to 0 bytes, or a new .php or .jsp file is created disguised as .jpg, initial response is delayed.
Improvements must be made along two axes. First, use a static analysis tool such as Semgrep to check during the PR stage whether calls to eval, base64_decode, system, passthru, or assert are mixed into the web application’s storage paths. Second, enable File Integrity Monitoring (FIM) across the entire web root through a HIDS solution such as Wazuh or OSSEC, and route any create or modify events straight to Slack as alerts. The rule set I recommend is as follows.
<syscheck>
  <directories check_all="yes" realtime="yes">/var/www/html</directories>
  <ignore>/var/www/html/wp-content/uploads/</ignore>
</syscheck>
With this configuration, the moment a .php file is uploaded, a log entry is written at the OS level and the EDR layer can take over for automatic blocking. Web shells are a threat you have to cut off at “just now” rather than “yesterday.”
Sarang Church Intrusion Path: Pre-Stolen Credentials and the SSO Trap
The situation at Sarang Church is different. Rather than an external web shell, account credentials already stolen from somewhere else were reused directly on the groupware server. After logging into the groupware, the attacker exploited the Single Sign-On (SSO) functionality to expand the reach into ERP. The names, addresses, and phone numbers of 286 staff members, including senior pastors, and 89,000 congregants were exposed.
SSO dramatically improves user convenience, but once a user passes authentication, every system behind it is bound to the same level of trust. The mistake I frequently see in the field is configuring MFA only at the front of the unified login while skipping authentication on backend ERP APIs on the grounds that they are internal IPs. Attackers target exactly this single-line allow rule. The same trap surfaced repeatedly in the parameter tampering analysis where missing authorization was the decisive variable. The key is to enforce re-validation of the SSO token’s issuer, audience, and exp claims on the backend.
Account-side controls must go hand in hand. Integrate dark web monitoring and Indicator of Compromise (IoC) feeds into your SIEM so that when a login is detected at an unusual time, from an unusual location, or with an unusual User-Agent, the session is forcibly terminated and a password reset plus MFA re-registration is required automatically. The following Splunk SPL rule can be run once a day to surface abnormal patterns.
index=auth action=success user=*
| stats values(src_ip) as ips values(user_agent) as ua by user
| where mvcount(ips) > 3 OR mvcount(ua) > 2
AI Agents Automated the Attack Documentation
The most noteworthy change in this incident is the evidence of AI usage. The attack process documents obtained by Oasis Security include references to “sub-agents,” and hundreds of attack handoff reports that synthesize system architecture and account information have been found. These are traces of attackers personally leaving notes for each stage. It is estimated that a separate, lower-cost AI model, different from the one used in the financial-sector hacks, was deployed.
This goes well beyond “using AI to write polished phishing copy.” It means an agent loop was operating in which the AI took in system structures, decomposed them into sub-tasks, fed back the execution results, and documented them. Because command execution, file discovery, permission checks, and data extraction were all automated, the manpower and time required per attack dropped dramatically. What would take a human several days can be compressed into a matter of hours by an AI agent.
The response must move toward behavior-based detection. Use UEBA to catch patterns in which large numbers of commands are executed in a short window, or large files are compressed and sent outbound through unusual paths, and use DLP to block outbound exfiltration traffic. Collecting EVE logs with Suricata and deploying the rule below alongside it is highly effective.
alert http $HOME_NET any -> $EXTERNAL_NET any (msg:"LARGE outbound zip upload"; flow:established,to_server; http.content_type; content:"application/zip"; byte_test:1,>,5242880; sid:2024101501; rev:1;)This single-line rule catches outbound zip transfers of 5MB or more, and when combined with normal office traffic patterns, it can surface abnormal exfiltration with very little noise.
Second-Stage Damage Scenarios: Smishing and Phishing Armed with Leaked Data
The first-stage breach is not the end. KISA’s Boho Nara service has warned of the possibility of second-stage attacks using the leaked congregant rosters and offering details as bait. According to the phishing advisory from Boho Nara, malicious URLs and search-result manipulation techniques using keywords such as “subsidy application,” “damage compensation payment,” and “leaked information check” have already been confirmed. Even if a real text message arrives, user education should include the fact that “KISA and financial institutions do not request installation of remote control apps via phone or text.”
When malicious app infection is suspected, the manual should be prepared in advance to guide users through this sequence: switch to airplane mode → run an approved antivirus scan → reissue public certificates and security cards. For mobile payment damages, the sequence is: obtain a carrier micropayment confirmation certificate → visit a police cyber investigation unit to obtain a case fact-confirmation certificate. If there is no incident response manual, cases repeat in the field where victims approve two or three payments within 24 hours.
What to Do Right Now
- Enable File Integrity Monitoring from Wazuh or OSSEC across the entire web root, and automate Slack alerts whenever new .php, .jsp, or .aspx files are created.
- Add Semgrep rules (p/php, p/java, p/python rules detecting eval, base64_decode, system, passthru, and assert) to the CI pipeline to block suspected web shell code at the PR stage.
- Enforce issuer, audience, and exp validation on every SSO backend API call, and combine MFA re-authentication with the internal IP whitelist.
- Integrate dark web monitoring and IoC feeds into the SIEM, and automate session termination plus password reset whenever a login is detected at an unusual time, from an unusual location, or with an unusual User-Agent.
- Use Suricata and EDR rules to behaviorally detect outbound transfers of 5MB or more and bursts of many commands in a short window, and use DLP to immediately block outbound exfiltration traffic.
A New Threat Built on Target Expansion and AI Automation
This church hacking incident redrew the line for “where the primary target ends.” Every non-financial, non-public institution that bundles ERP, groupware, approval, and donation DBs is already inside the target zone. Add AI agents to that, and attackers can try more places at lower cost while also lifting their success rate. The security team’s job is clear: block web shells at the code level, treat account trust as a per-request verification rather than a permanent state, and re-audit ERP backend authorization. Those three things form the first control line you can start drawing today.
Frequently Asked Questions
Small and mid-sized religious organizations have limited security budgets. Can tools like Wazuh and Semgrep really be operated for free?
Wazuh is an open-source HIDS that provides FIM and log aggregation features free of charge. The Semgrep community edition also includes core rules for detecting eval, base64_decode, and similar patterns. However, initial rule tuning and operational staffing are required, so a division-of-labor model in which detection rule operation is outsourced to an external MSSP while the in-house team handles only log collection and policy management delivers the best cost-to-effectiveness ratio.
Legacy ERP systems are hard to modify at the API level. How far can SSO backend validation realistically be enforced?
If you cannot directly modify the legacy ERP code, a realistic approach is to add a filter in front of the API Gateway that validates the JWT’s issuer, audience, and exp claims. Narrow the network boundary so that only traffic passing the authentication filter can reach the ERP, and leave backend call logs in the WAF for use as a post-incident audit trail. It is a key path for raising the control level without changing code.
Can AI agent-style attacks be stopped by EDR alone?
Not on its own. EDR catches process-level behavior, but data exfiltration rides inside normal HTTPS traffic. EDR plus UEBA plus DLP plus Network Detection and Response (NDR) must be operated together so that judgment is made through correlation rather than a single signal. Using EDR as the first line of blocking and DLP as the second is the most stable division of roles in practice.
Source Reference
This article was prepared with reference to the following original source: Boan News — “No Sanctuary from Cyberattacks”… Hacking Attacks Targeting the Religious Sector on High Alert
Leave a Reply