Category: Security News

  • Five Bank Chiefs Testify on Data Breach Response

    Five Bank Chiefs Testify on Data Breach Response

    The CEOs of five major banks will appear as general witnesses before the National Assembly’s Legislation and Administration Committee and the Financial Supervisory Service on the 19th to explain their response to the financial sector’s series of hacking incidents and measures to prevent recurrence. KB Financial Group CEO Lee Wan-joo, Shinhan Financial Group CEO Jung Sang-hyuk, Hana Financial Group CEO Lee Ho-seong, Woori Financial Group CEO Jeong Jin-won, and NH Nonghyup Bank CEO Kang Tae-young are reportedly reviewing the circumstances of the incidents and preventive measures in emergency mode, even over the weekend, as they prepare for the audit.

    Data Leak Circumstances and Management Accountability in Focus

    It will be the first time in four years that the five bank CEOs have appeared together as witnesses at an audit, since October 11, 2022. That hearing addressed financial misconduct, including embezzlement, and internal controls. This time, scrutiny is expected to focus on the circumstances surrounding customer data leaks caused by AI-enabled hacking, the incident response of the departments involved, security investments, and management’s accountability for oversight.

    The banks are consulting major law firms while conducting comprehensive system inspections and reviewing their security posture. They are also considering procedures to compensate customers quickly if additional damage occurs. However, the scope of the data leak and the specific method of attack have not been disclosed.

    From Inspections to Larger Budgets and Stronger Security

    The banks are refining their follow-up measures and security enhancement plans. During the audit, they plan to explain in detail how they are determining the causes of the data leaks and what steps they are taking on the ground to prevent recurrence. As security responses continue, there is also a possibility that additional, undisclosed hacking risks will be raised. Financial institutions hope the audit will serve as an opportunity to strengthen their information protection standards.

    There are expectations that discussions in the National Assembly on expanding security budgets and advancing related initiatives will reinforce banks’ security efforts. Meanwhile, some have raised concerns that the hearing could lead to excessive blame or create unnecessary fear. The terms of all five bank CEOs in attendance are scheduled to expire at the end of this year, meaning issues surrounding governance, including succession or contract extensions, may also be raised.

    A financial industry official said the audit should be a practical forum for advancing the industry’s security systems in response to AI-based hacking threats, rather than a venue that amplifies excessive blame or unnecessary customer anxiety. The details disclosed after the audit, including how the data leak occurred, where responsibility for the incident response lies, and whether security enhancement plans and the necessary funding are in place, will provide the basis for evaluating the completeness of the banks’ hacking response. When concrete action plans are presented, it will be necessary to determine whether the response to the hacking incidents will develop into a sustainable security system rather than temporary measures for each institution.

    Detailed coverage can be found in Security News’ article on the five bank CEOs appearing before the National Assembly’s Legislation and Administration Committee.

  • DB Savings Bank Data Breach Raises Security Concerns

    DB Savings Bank Data Breach Raises Security Concerns

    An incident believed to have exposed the personal data of 142 people at DB Savings Bank, including employees and project contractors, has occurred. The leaked information was reportedly used in an attempt to check loan limits, although no actual financial transactions took place. Because the data breach led to an attack involving financial transactions, access rights for outsourcing projects and post-transaction controls have emerged as key security management issues.

    Incident Timeline and Anomalous Access

    According to a Financial Supervisory Service incident and system failure report submitted to lawmaker Shin Dong-wook’s office on the National Assembly’s Committee on Policy and Administration, the incident occurred in the bank’s internet banking and mobile web systems. It began at 12:28 p.m. on the 10th and was detected at 6 p.m. the following day.

    Those affected included 122 employees, including retirees, and 20 project contractors. Four types of information were exposed, including internet banking user IDs, names, resident registration numbers, and mobile phone numbers. Contractors involved in the digital channel modernization project conducted since November 2024 were identified as a possible route for the data leak, but the circumstances surrounding their involvement and whether it was intentional have yet to be confirmed.

    Subsequent anomalous loan-limit checks followed the exposure of the information. DB Savings Bank said it had blocked all transactions in accordance with company policy and that no secondary damage had occurred as of the time of its statement. Following the incident, the bank added the attacking IP addresses to a firewall blocklist and continued monitoring for similar patterns.

    Contractor Access Management and Supply-Chain Security

    The central issue revealed by this case is that the impact of a personal data breach did not end when the data was initially exposed. The personal information accessed by contractors subsequently resulted in anomalous access, including loan-limit checks. In practical operations, it is important to manage project participants’ data access scopes, permission approval and revocation procedures, and activity records for personnel within the supply chain together.

    Firewall blocking and transaction blocking serve as evidence of defenses that prevented the activity from developing into actual financial transactions. However, blocking attacking IP addresses alone cannot eliminate every malicious access attempt, so a continuous detection system that distinguishes normal transactions from anomalous patterns is also necessary. Supply-chain management should likewise go beyond simply granting access and include verifying where personal information is being used.

    DB Savings Bank advised those affected to remain alert to secondary damage through unwanted methods, including spam and phishing emails. The bank said it would establish a compensation system through channels such as its customer center, the Personal Information Protection Commission, and the Financial Supervisory Service if actual damage occurs. The response to a personal data breach must extend beyond servers and firewalls, requiring follow-up security measures that connect affected individuals with guidance and victim compensation procedures.

    Security News’ report on the suspected DB Savings Bank personal data breach shows that access controls for contractors and anomalous transaction detection need to be combined to address this type of incident.

  • AOMEI Backupper Update Hijack Exposes Windows Backdoor

    AOMEI Backupper Update Hijack Exposes Windows Backdoor

    Attackers did not compromise AOMEI Backupper’s official update server for an extended period. Between May and July 2026, they changed files on the server for several minutes, causing Windows backup software that checked for updates during those windows to download and execute a malicious package. According to analysis by Google Threat Intelligence Group (GTIG), Mandiant, and ManageEngine’s Threat Analysis Lab, AOMEI fixed the server issue but did not guarantee that it would remove backdoors already installed on compromised systems. The incident showed how update-server tampering can create a brief intrusion window and exposed structural problems in a software supply chain where signed files alone cannot be trusted.

    Turning a Legitimate Update Path into a Malicious Delivery Channel

    AOMEI Backupper uses a background service to access AOMEI servers over HTTPS and check for updates and notification windows. This process is supported by two files, down_html.ini and Notifycfg.ini. down_html.ini specifies the update package to download and the checksum used for verification, while Notifycfg.ini determines what the notification service displays and executes.

    The problem was that neither file was cryptographically verified. Although the checksum was intended to prove that the downloaded package was authentic, it was stored in the same unsigned files that attackers could modify. Consequently, the presence of a checksum did not guarantee that the update server and metadata could be trusted. Analysis found that no vulnerability in AOMEI Backupper or separate user manipulation was used. By changing the two text files on the server for several minutes, attackers turned the legitimate update process into an execution path for a malicious package. Programs that checked for updates during that period downloaded the package to their folders and then executed it according to the notification settings. Execution followed the permissions of the AOMEI process.

    Three Attacks Detected Within Five to Ten Minutes

    GTIG and Mandiant identified three periods during which the attacker tampered with the server. Files were modified for 10 minutes on May 28 from 05:40 to 05:50 UTC, for six minutes on July 16 from 08:33 to 08:39 UTC, and for five minutes on July 20 from 10:35 to 10:40 UTC. Only copies that checked for updates during the tampering windows were affected, while copies that checked immediately before or after those windows were confirmed to have received legitimate files. This behavior could enable attackers to evade time-based automated analysis and file scanning.

    The attacks did not appear to target a particular country or organization. GTIG described the activity as opportunistic targeting in which systems that happened to check for updates at the relevant times became targets. The affected organizations identified through GTIG’s own telemetry spanned 11 countries in IT services, telecommunications, and higher education. The publicly named countries were Australia, Brazil, India, Pakistan, Portugal, Singapore, South Africa, Spain, Switzerland, Turkey, and the United States. The overall scope of the compromise has not been disclosed, but the actual number may have been higher than the confirmed figure. The report did not specify all affected versions of Backupper, while the version analyzed by ManageEngine’s Threat Analysis Lab was 8.3.0.

    Multi-Stage Remote Control Using Radmin

    On systems that received the malicious package, GTIG found that a downloader called CROSSROAD extracted files into a local Radmin folder. It then created a scheduled task that ran every three hours and deleted its own files from disk. The bundle included a legitimate, signed copy of Radmin, but it remained inactive on the analysis systems examined by ManageEngine. No listener, configuration, or new account was created, and actual remote control was handled by a separate implant.

    When the scheduled task ran the legitimate Radmin program, it loaded an attacker-created DLL from the same location, and the DLL executed the SHINYROAD implant. SHINYROAD provided a remote shell and could receive and execute additional code on command. The communication destination was identified as a single hard-coded address with no backup address, and blocking that address could sever the attacker’s control communications. However, blocking the address does not automatically resolve the exposure of credentials through WebDAV.

    CROSSROAD did not run identically on every system. It stopped execution when located in China, and ManageEngine also found that it stopped on systems with certain security agents installed. On some systems that passed these conditions, the open-source Adaptix C2 was additionally deployed on top of SHINYROAD and disguised as Nitro PDF software. AOMEI identified AnyViewer, a remote desktop tool that uses the same update flow, as a related target, but the publicly reported detections focused primarily on Backupper. GTIG tracks the attack group as UNC7017 and has not disclosed a country or known attacker affiliation.

    A Path to Expose NetNTLMv2 Without Code Execution

    The July 20 tampering also included a method that did not require execution of a separate program. The notification settings were changed to open an invisible one-pixel window that pointed to a WebDAV file on the attacker’s server. WebDAV allows remote files to be accessed as if they were on a local disk, and while Windows rendered the window, it could send the logged-in user’s NetNTLMv2 authentication response to the attacker’s address. This response is an authentication token that may be subjected to offline cracking or replay. Because there were few visible traces for users and no separate code execution occurred, information could already have been exposed even on systems where the backdoor was blocked.

    Gaps in Update Integrity Verification

    The central issue in this attack was not simply that the server was tampered with for a few minutes. Attackers could alter the update metadata, and clients followed the legitimate update process without cryptographically verifying that metadata. Organizations running AOMEI backup software should examine the times when updates were checked, the installation of Radmin, scheduled tasks running every three hours, SHINYROAD communications, WebDAV access, and unusual NetNTLMv2 traffic. AOMEI’s server-recovery report does not mean that the supply-side problem was fully resolved or that malicious persistence mechanisms remaining inside systems were removed. Unless the official update trust model adds signature verification and independent integrity checks, brief tampering with the update server can again turn a trusted software delivery path into a channel for remote control and credential theft.

  • OT Remote Access: From Asset Mapping to Verification

    OT Remote Access: From Asset Mapping to Verification

    As cases emerge of U.S. federal civilian agencies failing to properly inventory their operational technology (OT) assets, infrastructure security is shifting toward remote access control. Of the 22 agencies examined by the U.S. Government Accountability Office (GAO), seven failed to establish an initial OT asset inventory, while the other 15 failed to meet management standards because of inadequate maintenance and missing requirements. Across the full group, 68.2% lacked even minimal visibility into security controls for remotely connected devices, elevating risks surrounding remote access to a national security concern.

    These management gaps created more direct risks for water infrastructure. In late July, more than 30 water facilities across Minnesota were hit by coordinated cyberattacks that disabled control systems, with attackers gaining remote access to internet-exposed PLCs, changing IP addresses and passwords, and blocking legitimate operators from accessing the systems. The incident raised concerns about reduced water pressure and flooding, demonstrating that a cyber intrusion can lead not only to data theft but also to physical operational disruption and safety hazards. The White House has launched Project Watershed 250, a public-private initiative that began with Texas water facilities in September to assess remote-access vulnerabilities across national infrastructure.

    Control Directions Required by U.S. Regulation and NIST

    U.S. OT security controls are moving beyond recommendations toward enforcement. The Global OT Cybersecurity Consortium (OTCC) has issued a binding directive requiring CISA to mandate asset visibility, network segmentation, and remote access controls. OTCC noted that self-assessment methods alone struggle to close gaps involving remotely connected devices and urged the expansion of IT security regulations to OT and industrial control system (ICS) environments.

    Regulators have also released a security guide for remote access to water-sector OT. NIST SP 1800-45 identifies techniques that abuse remote payment channels or legitimate compromised accounts to manipulate PLCs and HMIs as the most severe threats. It therefore presented multifactor authentication (MFA) that does not rely on passwords alone, comprehensive network segmentation, logging of user activity, and session visibility as core requirements.

    The common thread across these standards is that blocking connections alone is insufficient. Because an attacker’s account and remote access channel may appear legitimate, organizations must be able to determine who connected, when they connected, and what authority they used to issue commands. An asset inventory provides the starting point for control, while user-level identification and audit logs transform remote access control from a retrospective record into a manageable policy.

    Legacy PLCs and the Availability Dilemma

    Deploying these controls in the field presents challenges because the strongest IT security measures cannot simply be transferred unchanged. Legacy PLCs that have operated for decades may struggle to handle complex authentication algorithms or security protocols directly, while national infrastructure must operate around the clock. Even slight communication delays or false positives caused by a security solution can trigger a full process shutdown, creating a conflict between improving security and maintaining operational stability.

    As a result, organizations are introducing control points at the front end without replacing existing PLCs. K-water is validating this approach with security company Sentstone through a performance-sharing agreement, deploying a security gateway in front of existing PLCs without modifying their firmware or control logic. Rather than strengthening the PLC’s own security features, this approach inspects incoming commands immediately before they reach the equipment.

    OT Security Shifts Toward Pre-Execution Controls

    Sentstone’s OTAC Trusted Access Gateway (TAG), used in the validation project, was deployed inline in front of the equipment. It dynamically verifies the identity and permissions of control commands from external remote users or internal operators immediately before they are forwarded to the PLC, using one-way dynamic code. The key is controlling unauthorized access through stolen accounts before it reaches the PLC, rather than merely raising alerts after a control command has been executed.

    In this structure, user identification and authentication serve as the starting point for connection control, and authentication results determine whether commands are permitted. The validation also demonstrated that user-based audit logs and implementation of IEC 62443 standards can be adapted to field environments. A method that verifies remote users and command-level authority without compromising the availability of existing equipment is being discussed as a model applicable not only to water facilities but also to critical national infrastructure that must operate over the long term.

    The change evident in the strengthening of U.S. regulation is more than an expansion of warning systems. Organizations must first determine what is connected, then identify who is accessing it, verify what permissions they hold, and record what they actually executed. This process cannot be completed through closed networks or post-event alerts alone. Building OT remote access control as one integrated system connecting policy, asset management, authentication, and audit logs remains the next security challenge.

    For background and further details, see Boan News’ report on OT security at U.S. federal agencies.

    Source Note

    This article was prepared after reviewing the following source: Boan News — 32% of U.S. Federal Agencies Lack Even a Basic Asset Inventory… Global OT Security Hits Its Limits

  • Financial Security Agency Revamps Homepage for 16 Services

    Financial Security Agency Revamps Homepage for 16 Services

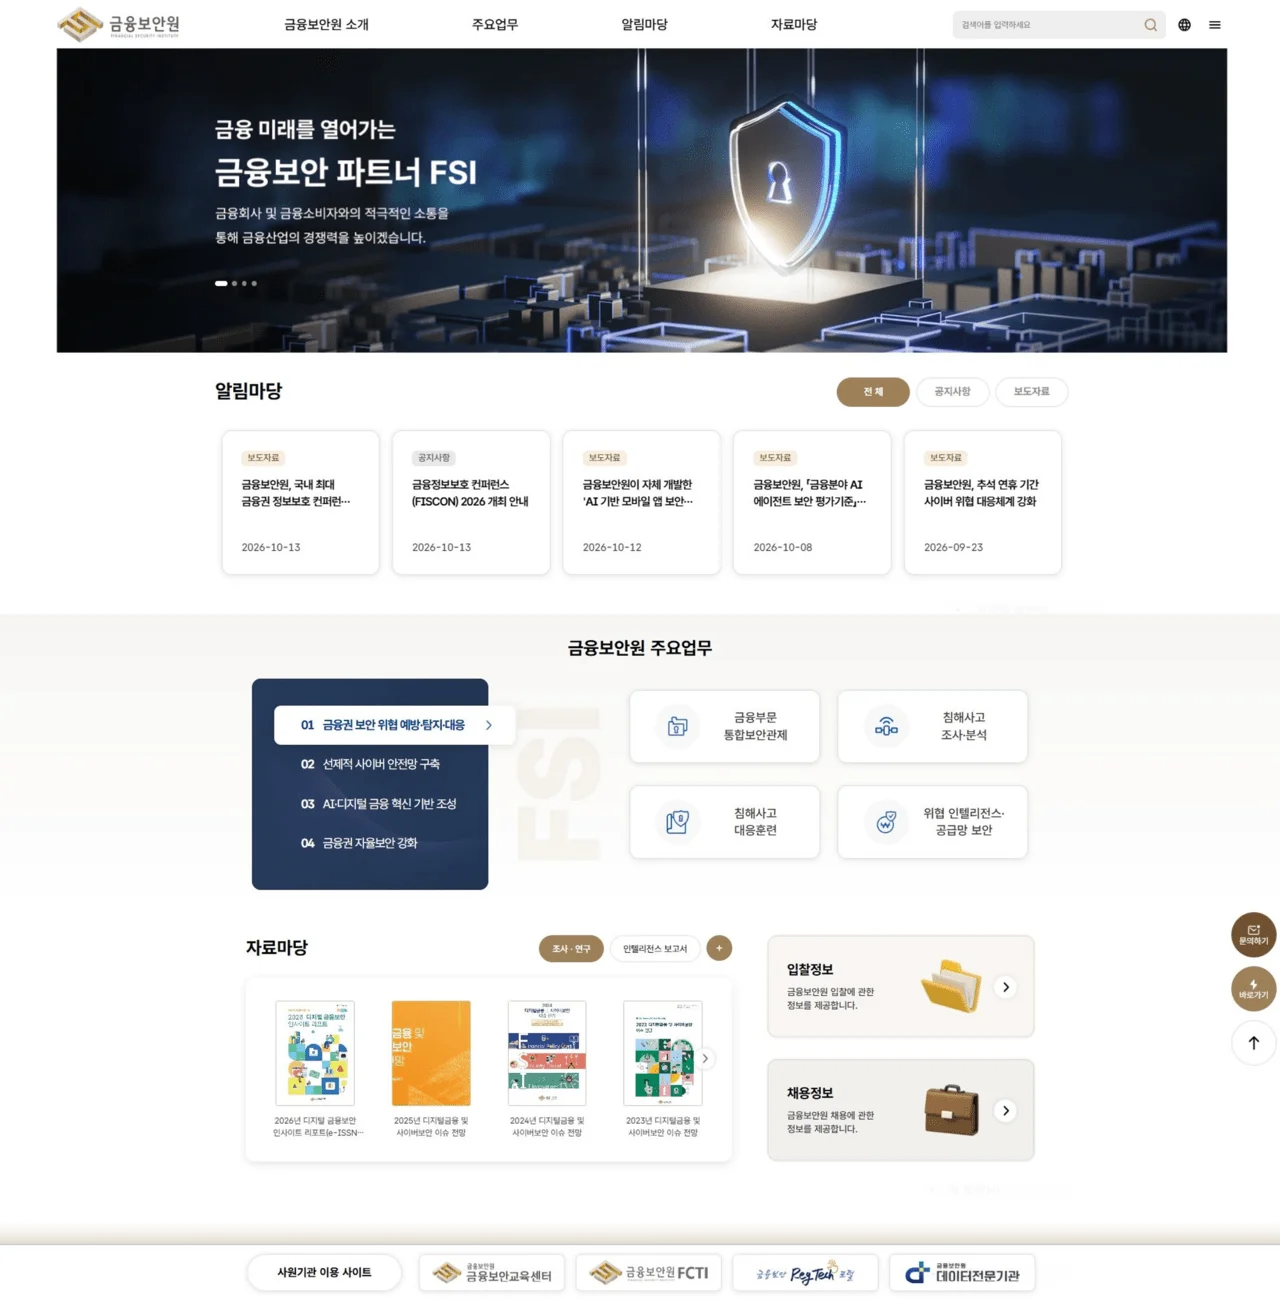
    Security News reported that the Financial Security Agency revamped its main homepage on October 16, 2026, to make official information and services easier to find. Notices and press releases were arranged as cards, while research materials and key services were reorganized with visual elements. The focus of the revamp was not new security features but improvements to the information architecture and navigation.

    Information Architecture by Category

    Key information and content that had been crowded onto a single page were divided into category-specific portals. For users unfamiliar with financial security, the Financial Security Agency created new content sections for 16 key services and revamped the top navigation. The move toward infographic-based explanations of the agency’s work appears focused on helping users understand complex services.

    Practitioners can check the responsible department and contact information for each service, along with related sites. A quick menu was also added to the bottom of the homepage to provide direct access to major sites operated by member institutions. Together, these elements show that the revamp covered not only finding information but also connecting users to the responsible department after locating what they need.

    Keeping Content Current in a Changing Environment

    The Financial Security Agency said it will promptly reflect future organizational and service changes on its website and continuously keep its content up to date. President Park Sang-won said, “We will continue to update the content in line with the changing financial security environment and further improve information accessibility and convenience from the user’s perspective”. This homepage revamp does more than display an updated list of services: it improves the structure for finding official information by connecting users with contact details and related sites.

    Original Source

    This article was written after reviewing the following source: Boannews — Financial Security Agency homepage revamp… Improved visibility and convenience

  • PwnEscape: Linux Kernel Flaw Lets Guests Read Host Memory

    PwnEscape: Linux Kernel Flaw Lets Guests Read Host Memory

    On October 15, 2026, security outlet The Hacker News reported a serious flaw in the Linux kernel that lets a packet sent from inside a virtual machine read the host’s memory. Tracked as CVE-2026-99999 with the alias PwnEscape, the vulnerability can produce three outcomes: guest-to-host memory exposure, host crash, and host code execution. Researcher Paulos Yibelo reproduced a memory leak demonstration in Vercel’s production sandbox, and Vercel confirmed it.

    The three demonstration outcomes and their limits

    Paulos Yibelo of security firm pwn.ai demonstrated in a technical report that a specially crafted network packet sent from a guest can trigger three behaviors: host memory read, host crash, and host code execution. All three outcomes stem from the same kernel flaw. Each packet sent from the guest leaked roughly 32 bytes of host memory, and the leak continued as long as packet transmission continued.

    However, the host crash and code execution were reproduced only in the researcher’s own lab environment simulating Vercel, and the researcher stressed, “This is not a claim of root command execution in any vendor’s production environment”. Two specially crafted packets were enough to crash the host and bring down all sandboxes on the same host, and the same flaw could be leveraged to reach administrative privileges on the host outside the VM. Vercel confirmed in the challenge report that the memory leak demonstration was performed in a production sandbox, but added that no customer files, secrets, or application data were reported to have been read.

    Rating and attack conditions

    Kernel maintainers assigned CVE-2026-99999 to this flaw and gave it a 9.3/10 Critical rating in the public record. The same record classified the attack vector as Local, specifying that an attacker must already be able to execute code inside the guest. In other words, this is not a flaw an outside party on the internet can exploit simply by sending packets. The flaw is not listed in the U.S. CISA Known Exploited Vulnerabilities catalog, and there are no reports of it being used in real attacks.

    Implications for shared infrastructure

    Vercel Sandbox runs each customer’s code in a Firecracker microVM with its own Linux kernel copy on a bare-metal Amazon EC2 host, and this microVM serves as the isolation boundary between customers and from the host. pwn.ai assessed that Vercel’s configuration is hardened above industry standard and that no misconfiguration was found. However, the flaw is not in that isolation boundary but in the networking code of the Linux kernel the host runs, so since nearly every major cloud separates customer workloads at the same Linux kernel layer, Vercel noted that the risk extends beyond a single provider to shared infrastructure broadly.

    The fix and operational notes

    The fix is a single kernel change commit 6785011f8b16 written by Michael S. Tsirkin of Red Hat, and it has been merged into mainline. The patch adds checks at five points in the networking code to ensure that checksum data does not point to a region before the IPv4 header before the kernel acts on the packet. The author described it as a “defence in depth” measure, adding that more complete validation at the point where packets enter the kernel requires additional work. Maintainers backported the fix to supported stable branches. Linux distributions ship their own kernels and often apply this kind of fix without changing the version number, so the version seen in uname is not enough; teams must check distribution security advisories and confirm the kernel the host is actually running includes the fix.

    Immediate practical steps

    First, the host’s Linux kernel should be updated to a version that includes the fix, or to a vendor build that includes it, and the host rebooted. Updating only the guest kernel does not resolve the host’s flaw. If a patch cannot yet be applied, narrowing the blast radius when a compromise occurs is the typical fallback. Vercel noted that its own mitigations are keeping the host kernel up to date, disabling nested virtualization, and using the Firecracker jailer to grant microVM processes only the privileges they need; this does not fix the flaw itself but is intended to limit what an attacker who succeeds can do. The original report did not present a separate workaround.

    AI-assisted research and challenge reward

    This flaw was discovered during Vercel’s two-week sandbox breakout challenge in August, which offered a total of USD 1 million in prize money. The per-report cap was USD 50,000, and Vercel paid out a total of USD 242,000 across 1,285 reports; this flaw was the only Critical verdict among them. pwn.ai said it used its AI-assisted research system Omega-Pwn along with GPT-5.6 Sol and SingularityNET’s OmegaClaw components to find the flaw in three days, with an API token cost under USD 700. This case adds to a recent trend showing large language models being used in real Critical-rated flaw discovery.

    Reference source

    This article was prepared by cross-checking the following source: The Hacker News — Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory

  • 1,413 Patches, 1 Exploit: Microsoft’s New October Triage

    1,413 Patches, 1 Exploit: Microsoft’s New October Triage

    On October 14, 2026, Microsoft broke its own Patch Tuesday record by patching 1,413 vulnerabilities in a single release. But what stands out as much as the sheer volume is the priority that separates them. Only one flaw was confirmed as actively exploited, and Microsoft introduced a new triage approach called “risk cohorts,” which groups similar flaws together for joint evaluation. The era of patch volume is effectively over; the ability to determine which flaws to patch first through patch triage now defines the success or failure of security operations.

    One Exploit and the Core CVE Set

    The flaw confirmed as actively exploited in this month’s release is a single vulnerability: CVE-2026-96951 (Windows Shell command injection, CVSS 8.8). Attackers can leverage this vulnerability to bypass the Mark of the Web (MOTW) defense, with scenarios that send specially crafted files via email or messenger to lure users into opening them. Attackers cannot, however, force user action; user manipulation such as clicking a link or opening an attachment is required. Microsoft attributed the discovery of this flaw to Riku Bamba and Yuya Chudo of Fujitsu, Benoit Sevens of Anthropic, and researcher yhw. The U.S. CISA added CVE-2026-96951 to the Known Exploited Vulnerabilities (KEV) catalog and required U.S. federal agencies to apply the patch by October 16, 2026. The details of the actual attacks and the targeted organizations have not been disclosed.

    Two other flaws were publicly disclosed at the time of patching. CVE-2026-108398 (.NET Framework unsafe search path, CVSS 8.8) allows an authenticated attacker to register a specially crafted.NET assembly on the system and execute arbitrary code within a protected process, bypassing Windows Defender Application Control (WDAC). Because no separate user interaction is required, this technique is rated as particularly dangerous at the post-compromise stage. This flaw was discovered by James Forshaw of Google Project Zero. CVE-2026-92707 (MessagePack-CSharp memory allocation flaw, CVSS 5.3) was patched following a report from an anonymous researcher and is the second publicly disclosed flaw of the month; it can cause denial of service on the network.

    Beyond these, Microsoft also patched a CVSS 9.8 Raw Image Extension heap-based buffer overflow (CVE-2026-21413). The flaw is triggered simply by navigating to a folder containing RAW image files and having previews or thumbnails generated, meaning it is dangerous even without opening the file itself.

    The Composition of 1,413 Patches and the 4,000 Era

    Breaking this month’s 1,413 patches down by product: Windows 1,102, Office 134, Developer Tools 61, SharePoint Server 36, and SQL Server 22. By impact type, the release includes more than 670 elevation-of-privilege, over 300 remote code execution (RCE), and over 250 information disclosure flaws, with at least 70 rated Critical. Following roughly 1,000 patches in September, the tally also shows that the number of CVEs Microsoft has handled this year has surpassed 4,000.

    Dustin Childs, head of threat awareness at the Zero Day Initiative (ZDI), diagnosed that “the appearance of hundreds of CVEs in a single release is no longer an exception but the baseline”. Childs noted that AI is accelerating bug hunting on both sides, analyzing that “AI doesn’t conjure bugs out of thin air, but the gap between when a vulnerability exists and when someone notices it is narrowing”. Ultimately, the more important fact than the volume of patches being produced is that discovery is scaling faster than exploits, and teams that prioritize purely by CVE count are spending energy on the wrong flaws. Childs added, “Patch the disclosed flaws that are proven and prioritized first, and treat the rest under this month’s new baseline”.

    Risk Cohorts — Microsoft’s New Prioritization Tool

    Alongside this update, Microsoft introduced a new prioritization approach called risk cohorts. According to the company, a risk cohort is “a group of CVEs that need the same customer assessment”, with the caveat that “it is a starting point, not a final decision. You must review active exploitation status, severity, attack vector, user interaction, and per-product guidance together”. In other words, the assessment is made at the cohort level, but the decision must be applied to each individual CVE.

    This change aligns with the diagnosis from Adam Barnett, senior software engineer at Rapid7. He assessed that “the sheer volume of recent Patch Tuesday releases includes remarkable cases in itself, and those cases might have each received more attention in the lower-volume era”. As patch counts grow, the requirement follows that the patch triage procedures themselves — which flaws to address first — must be operated with greater precision.

    The Patch Triage Practitioners Must Rebuild

    Restructuring this month’s patch queue from an operational perspective, the top compresses into three items: (1) CVE-2026-96951 confirmed as actively exploited, (2) CVE-2026-108398, which bypasses WDAC and executes arbitrary code in a protected process without user interaction, and (3) CVSS 9.8 CVE-2026-21413, which is triggered simply by folder preview. The rest can be grouped under “this month’s new baseline” and quietly folded into the baseline. The October 16 deadline assigned to U.S. federal agencies for flaws listed in CISA KEV serves as a valid external benchmark for private-sector companies when setting priorities.

    A recent example of the same trend is the Vghost flaw (CVE-2026-74580) discovered in the Linux kernel vhost subsystem. Tencent’s Zhuque Lab released the patch on August 3 and published a detailed analysis alongside it on October 12, but no public exploit indicators have been confirmed yet. As AI accelerates flaw discovery on both sides, the only path for operational organizations to keep up is to increase the precision of patch triage. Microsoft’s core message is simple: in an era where discovery scales faster than exploits, the era of patch priority has already begun.


    References: Microsoft Patches Record Flaws, Including Exploited Windows Shell Bug · AI found Linux kernel flaw that gives local users root across nearly a decade

    Source Reference

    This article was prepared after reviewing the following original source: The Hacker News — Microsoft Patches Record 1,413 Flaws, Including Exploited Windows Shell Bug

  • GhostAction Returns: Fake Audits Steal GitHub Repo Secrets

    GhostAction Returns: Fake Audits Steal GitHub Repo Secrets

    The GhostAction campaign, first detected in September 2025, has returned with a second wave. As of the 9th, Socket’s investigation confirmed that more than 500 GitHub accounts pushed malicious workflows named ‘security-audit.yml’ and ‘github_actions_security.yml’ to tens of thousands of repositories. The workflows extract 13 types of credentials from registered secrets, repository working folders, and the full Git history, then transmit them via unencrypted HTTP to an external server (193.32.204[.]199). According to GitGuardian’s tally, 2,577 secrets have been exposed across 772 public repositories.

    How the Malicious Workflow Operates and the Intrusion Path

    GitHub Actions has the authority to execute arbitrary code inside a repository, meaning even a single-line workflow compromise leads directly to the immediate exfiltration of all registered secrets. The two files used in this attack run only a single ‘Audit’ step and are triggered by workflow_dispatch (manual execution) and unfiltered push events. In CI logs, they are nearly indistinguishable from legitimate audit jobs.

    The malicious step first reads Actions secrets registered on the repository and organization, then scans the working folder and the full Git history, using regex-based pattern matching to extract credentials. The 13 targeted patterns include AWS access key IDs (paired with their secret keys), generative AI service API keys such as Anthropic’s sk-ant-, OpenAI’s sk-, and OpenRouter’s sk-or-, GitHub ghp_ tokens, GitLab glpat- tokens, and PyPI, npm, and Docker Hub publishing tokens. The collected data is sent to the external IP via HTTP POST without any encryption.

    According to Socket’s analysis, the workflow was deployed to 27 repositories starting at 13:20 UTC from the account of Takashi Kitao, a Pyfhel developer. About 8 hours later, the same file was pushed to 318 repositories within 16 minutes from the account of Henry Wu (original author of athenadriver). At the time of the Henry Wu account compromise, 279 of his forks had already been injected with the same file, and subsequent sync operations by downstream forks could inherit the malicious workflow. Any repository with GitHub Actions enabled will automatically re-run the secret collection procedure on the next push. The initial intrusion path is believed to involve theft of the maintainer’s GitHub credentials (personal access tokens, PATs), with tokens harvested from infostealer malware logs or past breach data being reused directly for workflow reconnaissance.

    Spread Scale and Exposure Comparison vs. the First Campaign

    While the GhostAction 2nd wave is directly connected to the first attack, it shows clear differences in impact scope and targeting. The first campaign showed no attempts to deliver separate payloads beyond secret exfiltration, whereas the second wave has made npm, PyPI, and Docker Hub tokens primary collection targets, raising the possibility of follow-on supply-chain attacks via package registries.

    Category GhostAction 1st Campaign GhostAction 2nd Campaign
    Discovery Date Early September 2025 After September 7, 2025
    Affected Accounts 327 GitHub users 500+
    Compromised Repositories 817 772 public repositories
    Exposed Secrets 3,325 2,577
    Primary Targets Focused on PyPI, npm, Docker Hub tokens Expanded to AWS, Anthropic, OpenAI, OpenRouter, GitHub, and GitLab tokens
    C2 Communication Unconfirmed 193.32.204[.]199 (HTTP)

    No cases of malicious packages being published using the deployment credentials stolen in the second wave have been officially confirmed. GitGuardian tallied that public repositories belonging to 373 users and organizations were targeted between August 31 and September 30.

    Compromise Assessment, Immediate Response, and Recurrence-Prevention Framework

    The starting point for compromise assessment is the presence of the files. Check whether security-audit.yml or github_actions_security.yml was added to any repository after August 31, and immediately delete the file from all branches, forks, and mirrors upon detection. Cross-reference the IP addresses and User-Agent strings from the ‘Audit’ step in Actions logs to trace additional spread paths, and register the indicators (IPs, file names) published by GitGuardian, Socket, and StepSecurity as IOCs for continuous SIEM monitoring.

    Exposed credentials must be revoked and reissued immediately. This applies not only to GitHub PATs and SSH keys, but also to all repository and organization secrets, plus AWS, Anthropic, OpenAI, OpenRouter, PyPI, npm, and Docker Hub tokens. Enable Secret scanning and Push protection in Settings > Code security and analysis, and configure Dependabot secret scanning to automatically detect leaked secrets. Force Actions > General > Workflow permissions to ‘Read repository contents and packages’ and set the default GITHUB_TOKEN permissions to read-only.

    For the long term, AWS and cloud authentication should be migrated to OIDC federation so that access keys are no longer stored in repository secrets. When referencing third-party Actions, pin to a commit SHA rather than a tag, and automate SHA updates with Renovate or Dependabot. Protect the .github/workflows directory with CODEOWNERS to block indiscriminate PR merges, and for forks from untrusted sources, disable Actions or apply an allow-list to control automatic inheritance. The same logic applies to applying branch protection (Required reviewers, Required status checks) to externally dependent workflows.

    Remaining Risks and the Possibility of Supply-Chain Follow-On Attacks

    The GhostAction incident clearly demonstrates that when the structural permissions of GitHub Actions combine with the auto-sync characteristics of the fork ecosystem, a single compromise can amplify to tens of thousands of repositories. The fact that respected developer accounts were abused as conduits, and that PRs were likely merged under the plausible pretext of a ‘security audit’, vividly illustrates how dangerous merge policies without external source verification can be. The consolidated tracking results from Socket, StepSecurity, and GitGuardian reported by Boannews confirm that even a single workflow intrusion can lead to large-scale credential exfiltration.

    Follow-on threats around the exposed credentials are also a variable. As long as the credential pairs remain valid, malicious packages can be published to registries like npm, PyPI, and Docker Hub to attack downstream users through supply-chain compromise. Although no publication incidents have been confirmed yet, registry-side token rotation and package integrity verification must be carried out promptly from the moment of compromise to prevent a secondary incident. The fact that this incident’s attack surface was compressed into a single workflow ties directly to the environmental context highlighted by the Korea Cybersecurity Gap diagnosis. Without a system that regularly audits repository secrets, workflow permissions, fork synchronization, and Action SHA pinning as a single bundle, predicting the next target is virtually impossible.

  • AI Agent Permission Control: 3 Axes to Stop Data Leaks

    AI Agent Permission Control: 3 Axes to Stop Data Leaks

    A common question comes up frequently in security teams: “We blocked ChatGPT, so why is internal data still leaking?” Despite deploying URL blocking, DLP regex, and employee training, leak incidents continue. When the root cause is traced, the problem is not what employees type into their browsers—it is the officially approved internal AI agent that holds broad OAuth scopes to Drive, SharePoint, and internal databases while calling LLMs. Policies that only block consumer LLM websites can no longer explain governance.

    Existing AI blocking policies all assume ‘human’ behavior. Consumer LLM domain blocking, prompt payload regex, and endpoint keyloggers are all designed to catch the moment an employee types or pastes something in the browser. Officially approved agents, however, operate through a different path. They receive tokens through OAuth flows, connect directly to company data stores via standard interfaces such as MCP, and their permissions are indistinguishable from a person accessing data individually. When full Drive read access is granted once to an agent service account, the agent can perform legitimate work like ‘contract review’ while simultaneously pulling HR evaluations and undisclosed financial data from other folders into the LLM context.

    Why blocking alone is not enough—the real leak path is ‘delegated permissions’

    To close this gap, AI agent permission governance must be redesigned around ‘agent identity’ rather than ‘human input.’ The core is ① minimum scope per agent, ② service accounts separated by work unit, ③ proxy-based token-level DLP and bidirectional logs—operating these three axes simultaneously. Enforcing only one axis lets leaks route around through another path, and organically combining minimum-privilege scope, dedicated identity, and bidirectional audit logs is what field practitioners agree creates real effectiveness.

    From the blocking policy’s perspective, there is no signal to distinguish whether the call is legitimate work traffic or a data exfiltration attempt. As a result, even the most sophisticated enterprise DLP creates a situation where incidents cannot be traced after the fact. The center of gravity in governance must shift from ‘where is it called from’ to ‘whose credentials delegated which scope.’

    Scope—Slice AI agent permissions down to the work unit

    The first area to address is the Drive, SharePoint, and RDB IAM policies. When an agent receives a task such as ‘review Company A’s contract,’ dynamic scopes should be granted so that only the folder and table mapped to that ticket are read- and writable. AWS Bedrock Agents limits the call context through IAM session policy and encrypts model invocation logging with KMS for retention. Azure AI Foundry and Google Vertex AI Agents similarly require, as a standard, managed inference endpoints with an explicit Zero Data Retention option, where data is inferred only within the customer tenant.

    # Enforcing per-agent scope via LiteLLM Proxy policy headers (Illustrative Example, not official spec)
    # In production, replace with IdP group and IAM role mapping
    curl -X POST http://litellm.internal/v1/chat/completions \
      -H "Authorization: Bearer $AGENT_TOKEN" \
      -H "X-Agent-Scope: drive:folder/CONTRACT-2026-Q4-A" \
      -H "X-JIT-TTL: 900" \
      -d '{"model":"claude-3-5-sonnet","messages":[{"role":"user","content":"Summarize the key clauses of the Company A contract"}]}'
    

    Scope should be cut not at the ‘agent ID’ level but at the ‘work ticket ID’ level. A short TTL of 15 to 30 minutes is granted, and the design ensures automatic revocation after expiration. Each time the same agent receives a new task, new temporary credentials must be issued. The pattern of granting a large OAuth scope at once and narrowing it later makes post-incident response nearly impossible. The immediate-revocation pattern covered in AI Agent Identity Separation: 5 Steps to Immediate Revocation is the starting point for this stage.

    Identity—Separate service accounts by work and integration unit

    Even when scopes are sliced finely, if it is unclear ‘whose permissions’ they are being invoked under, post-hoc traceability breaks. If the same agent handles HR, sales, and engineering integrations all together, audit logs cannot separate which data went out under whose authority. The standard pattern is to issue dedicated service accounts for agents at the IdP (Okta, Entra ID) level, and to maintain a separate workload identity for each integration and project.

    Session tokens must record the calling principal, work ticket, and expiration time, and this information flows to the LLM gateway and is automatically joined with downstream logs. Human accounts and agent accounts must follow clearly different lifecycles. Human accounts are revoked at termination, but agent accounts must have their tokens recalled as soon as a task ends. Separating identity naturally follows when applying the workload identity federation and periodic key rotation principles from the 90-day zero-trust roadmap emphasized in the MFA limits and bypass response article.

    Audit—Combine the LLM gateway with enterprise DLP

    The third axis is bidirectional logging. All outbound traffic to OpenAI, Anthropic, and Google APIs is funneled through gateways such as LiteLLM Proxy, Portkey, and Cloudflare AI Gateway for token-level inspection. Not only prompts but also responses must be retained as logs on the same gateway, so that post-hoc reproduction of “which data was sent to which external LLM in what form” is possible. Enterprise DLP solutions such as Microsoft Purview DLP, Palo Alto Networks AI Security, and Harmonic Security detect PII, customer code, and internal hostname patterns in front of this gateway.

    Gateway Deployment Key features Suitable environment
    LiteLLM Proxy Self-hosted OpenAI-compatible API, multi-model routing, token-level DLP hooks Multi-cloud, Kubernetes-friendly
    Portkey SaaS + self-hosted Observability, fallback, A/B routing, policy engine LLM workflow standardization
    Cloudflare AI Gateway SaaS DDoS protection, caching/cache invalidation, Workers integration Cloudflare ecosystem-dependent organizations
    # LiteLLM config excerpt (Illustrative Example, not official spec)
    model_list:
      - model_name: claude-3-5-sonnet
        litellm_params:
          model: bedrock/anthropic.claude-3-5-sonnet-20241022-v2:0
          aws_region_name: ap-northeast-2
          aws_session_token: os.environ/JIT_AGENT_TOKEN
    litellm_settings:
      drop_params: true
      request_timeout: 30
      success_callback: ["prometheus", "s3"]
      failure_callback: ["slack"]
    general_settings:
      drop_params: true
      master_key: os.environ/LITELLM_MASTER_KEY
    

    Unidirectional auditing that only collects prompts without logging responses is the most common anti-pattern. Even when an actual data leak occurs, it cannot be proven after the fact that “internal data was included in the external LLM response and returned.” Response logs must also be retained, but a retention policy must be set to automatically expire and cryptographically erase after 30 to 90 days to also address GDPR and personal information protection law compliance. Both LiteLLM and Portkey can stream logs to S3, GCS, and BigQuery, so folding them directly into an existing SIEM pipeline is the way to reduce operational burden.

    Endpoint and network secondary/tertiary defense layers

    If the three axes are the first line of defense, enterprise browsers, EDR, and CASB form the secondary and tertiary defense layers. Microsoft Edge for Business, Chrome Enterprise Premium, and Prisma Access Browser classify the generative AI site category and block personal account logins. EDR solutions such as CrowdStrike and SentinelOne trigger blocks and alerts when unknown agent harnesses (AutoGPT variants, local LLM clients, etc.) are installed. SaaS CASB solutions (Microsoft Defender for Cloud Apps, Netskope) track the flow of Drive shared links into AI workflows.

    The key value of this layer is ‘visibility into bypass paths.’ Even when the agent is not an officially approved one covered by first-line controls, it catches the moment an employee installs a local LLM client on their laptop or signs up for a Shadow AI SaaS with a company email. It does not prevent leaks on its own, but it becomes the baseline that distinguishes legitimate traffic defined by first-line controls from abnormal traffic. Combined with zero-trust NAC, calls to the gateway from devices whose posture does not meet requirements can be rejected entirely, serving as a safety net for first-line controls.

    Vendor governance and legal review

    Separate from technical controls, AI vendors must be explicitly named as sub-processors in contracts, and the Zero Data Retention option must be made mandatory. Standard clauses should include a provision that inputs and outputs from LLM API calls are not used for vendor training, a 72-hour incident notification obligation, and an audit log delivery obligation. AWS Bedrock, Azure OpenAI Service, Anthropic Enterprise, and Google Vertex AI all offer explicit ZDR options, but even when calling the same model, the retention policy differs by API key type (e.g., a general API key versus an Enterprise tenant key), so operations and legal teams must review together.

    Operational limits and common anti-patterns

    Five anti-patterns frequently seen in the field are summarized below. If even one of these is missing, post-incident response is effectively impossible.

    Anti-pattern Actual impact Correct pattern
    Granting full Drive read OAuth to an agent then narrowing it later Cannot reproduce which folders were accessed post-hoc Ticket-level Just-in-Time scope
    Bypassing security review citing only work efficiency Shadow AI spreads, responsibility unclear Mandatory security team approval gate
    Business unit alone decides on AI tools No catalog, duplicate introduction Internal AI catalog + central governance
    Direct LLM API call without a proxy Loss of token-level DLP and cost visibility LLM gateway standardization
    Collecting only prompt logs Cannot prove response data leakage Request/response bidirectional logs + retention

    On the cost side, additional infrastructure costs arise from introducing the LLM gateway and managed inference endpoints. LiteLLM Proxy is at the container cost level when self-hosted, but as traffic grows, Redis and Postgres backends must also be operated. Portkey and Cloudflare AI Gateway start with SaaS pricing, but cost increases linearly for large-scale log retention. Bedrock, Foundry, and Vertex themselves also apply per-token billing, so controlling token usage through scope minimization directly equates to cost optimization. In terms of cross-team collaboration, the RACI where the security team defines only scope policy and agent developers automate it through IaC has the fewest conflicts.

    What to do right now

    • Build an inventory of AI agents operating in-house, and map the OAuth scopes each agent holds to the connected data stores.
    • Check network logs for one week to see if there is any traffic directly calling OpenAI, Anthropic, or Google APIs, and add firewall rules to force-route all of it through the LLM gateway.
    • Pilot-deploy LiteLLM Proxy or Portkey scoped to one workflow, and verify that bidirectional logs for prompts and responses are delivered to S3 or SIEM.
    • Issue dedicated service accounts for agents from the IdP, and reorganize them into groups and policies separate from existing human accounts.
    • Create a quarterly agent permission audit process, and reflect in IaC the automatic revocation of unused scopes, expired tokens, and accounts linked to departed employees.

    The essence of in-house AI security ultimately boils down to the question, “How far, under whose authority, and for how long should data be entrusted?” As the field’s concerns discussed in the original thread show, blocking policies alone can no longer explain governance. Splitting AI agent permissions across the three axes—scope, identity, and logs—and building a structure that combines at least six detailed controls (dynamic IAM, dedicated SAs, bidirectional proxy, token DLP, temporary credential revocation, storage encryption) on top of that three-axis governance is the most realistic starting point for bringing data leak incidents into a post-hoc traceable state.
    Source

    This article was written after checking the following original thread: r/AskNetsec — How do you let staff use AI without company data leaking out?

  • ClosedQuorum AI Malware: Block LLM API Calls at Endpoints

    ClosedQuorum AI Malware: Block LLM API Calls at Endpoints

    A self-directed AI malware strain dubbed ‘ClosedQuorum’ that calls commercial LLM APIs to generate its next move in real time has been reported to the security community. Because the malware relies on an LLM to produce a fresh command at every step rather than running a fixed script, traditional detection systems built on signatures, static patterns, and behavioral rules are effectively neutralized. The first line of defense against incident spread is shifting away from more sophisticated detection rules and toward outbound controls that cut off unauthorized AI API calls at the endpoint and validate the dynamic commands returned by the LLM just before execution.

    Reasoning Malware: How ClosedQuorum Works

    After breaching an internal network, traditional malware typically branches its behavior by receiving pre-written commands from a C2 server. ClosedQuorum takes this model one step further: it calls a commercial large language model API and uses the inference result as its next command. The attacker packs the infected host’s system information, privilege state, and network environment into a prompt, sends it to the API, and the LLM generates the next intrusion procedure on the fly.

    What makes this approach dangerous is that the same sample is very unlikely to appear twice. Because every command is generated as the LLM’s inference output, there are essentially no hashes, strings, or YARA patterns for antivirus or EDR solutions to match. Communication with the LLM travels as a JSON payload over the standard HTTPS port 443, making it visually indistinguishable from ordinary cloud API traffic. Analysis shows that simple DPI or port-based blocking, and even traffic statistics, struggle to separate it from legitimate services. The same risk has already been confirmed in a case where a ‘silent intrusion’ compromised six 1st and 2nd-tier financial institutions within 72 hours, indicating that the attack surface of AI-driven intelligent intrusions is expanding across industries.

    Why Traditional Detection Systems Fail

    Traditional malware detection rests on three main pillars: signature and static analysis, behavior-based rules, and sandbox dynamic analysis. When an LLM generates a new command string on every call, as in ClosedQuorum, all three pillars lose their decisive clues. Even if an EDR tracks the activity of script hosts such as PowerShell, Python, curl, wget, Node.js, and rundll32, the payload content that their child processes emit changes every moment, so rule matching effectively cannot be applied.

    Around the same time, BoanNews reported that approximately 34,000 customer records had been leaked from Kakao Golf Reservation. The exposed fields included names, phone numbers, product names, round dates, payment amounts, order numbers, payment and cancellation timestamps, and virtual account numbers; Kakao VX noted that card numbers and resident registration numbers were not included. Although the two incidents differ in intrusion path and motive, the fact that LLM-mediated intelligent intrusions and conventional web application data leaks now coexist within a single threat landscape has led to assessments that security operations have grown more complex by a tier. The BoanNews card-news article that first reported ClosedQuorum explicitly identified ‘blocking unauthorized AI API calls at the endpoint’ and ‘strict outbound controls’ as the first line of defense in this shifting environment.

    Blocking LLM API Calls at the Endpoint: Redesigning the First Line of Defense

    The starting point of the ClosedQuorum response is cutting off unauthorized LLM API calls at the endpoint. The first policy applied is process tree-based control. In the EDR, configure detection and blocking at the child-process level for script hosts such as PowerShell, Python, curl, wget, Node.js, and rundll32 when they invoke HTTPS to commercial LLM API endpoints. Because simple domain blocking is easy to bypass, it is essential to also log which parent process issued the call and with which argument string.

    Host firewalls should be hardened in parallel. On Windows Defender Firewall, Linux nftables, and macOS pf, register the domains and IP ranges of major commercial LLM APIs in the block list for unauthorized processes, and allow only trusted processes on the whitelist as exceptions. It is generally recommended to pre-allow the administrator VPN range so that operator access is not severed during an emergency block.

    At the network layer, SSL inspection plays a decisive role. Apply a client-certificate-based whitelist to outbound HTTPS traffic through a proxy or SSL inspection appliance, and terminate port 443 communication with unapproved endpoints at the policy level. Because LLM calls look identical to legitimate cloud traffic on the wire, system commands inside the payload (whoami, ipconfig, registry keys, Base64 payloads, Shadow Copy deletion commands, and so on) cannot be detected without SSL inspection capable of plaintext inspection.

    Multi-Layered Defense: Outbound Controls and Runtime Validation

    Endpoint blocking alone is not enough. Once a single endpoint is compromised, the dynamic commands returned by the LLM can be used to attempt lateral movement to other hosts in the same subnet, and the collected data can be exfiltrated disguised as another normal API call. East-west traffic monitoring and network segmentation must be designed together to prevent the chain spread of LLM-based C2.

    SIEM correlation analysis should run in parallel. A rule that combines EDR script execution logs with SIEM network logs to automatically trigger an alert when a payload sent to an LLM API contains system command patterns is decisive for operational efficiency. It is recommended to enable the generative AI app control features of DLP and CASB solutions (for example, Microsoft Defender for Cloud Apps, Zscaler, and Netskope) to gain visibility into unauthorized LLM traffic and to extend inspection scope into the command patterns inside text payloads.

    The last line of defense is runtime control, which validates commands from the LLM just before execution. Before script hosts run externally received code, the code must pass through a whitelist-based command filter, argument normalization, and least-privilege enforcement. The incident response playbook should add a ‘suspected AI-API-driven intrusion’ scenario and explicitly include procedures for immediately isolating infected endpoints from the network, revoking LLM API credentials, and inspecting all endpoints within the same subnet and EDR group.

    In the age of AI malware, the center of gravity in security is shifting from ‘keep threats out’ to ‘keep data from leaving.’ In an environment where signatures disappear and behavioral rules miss every time, traditional controls such as endpoint and network outbound controls, SSL inspection, and runtime command validation are once again rising as the first line of defense. Because victory or defeat is determined by the gap between the speed of LLM-driven intrusion and the speed of operational controls, security organizations face the challenge of continuously updating their policies and playbooks to match the pace of LLM-based attacks.