
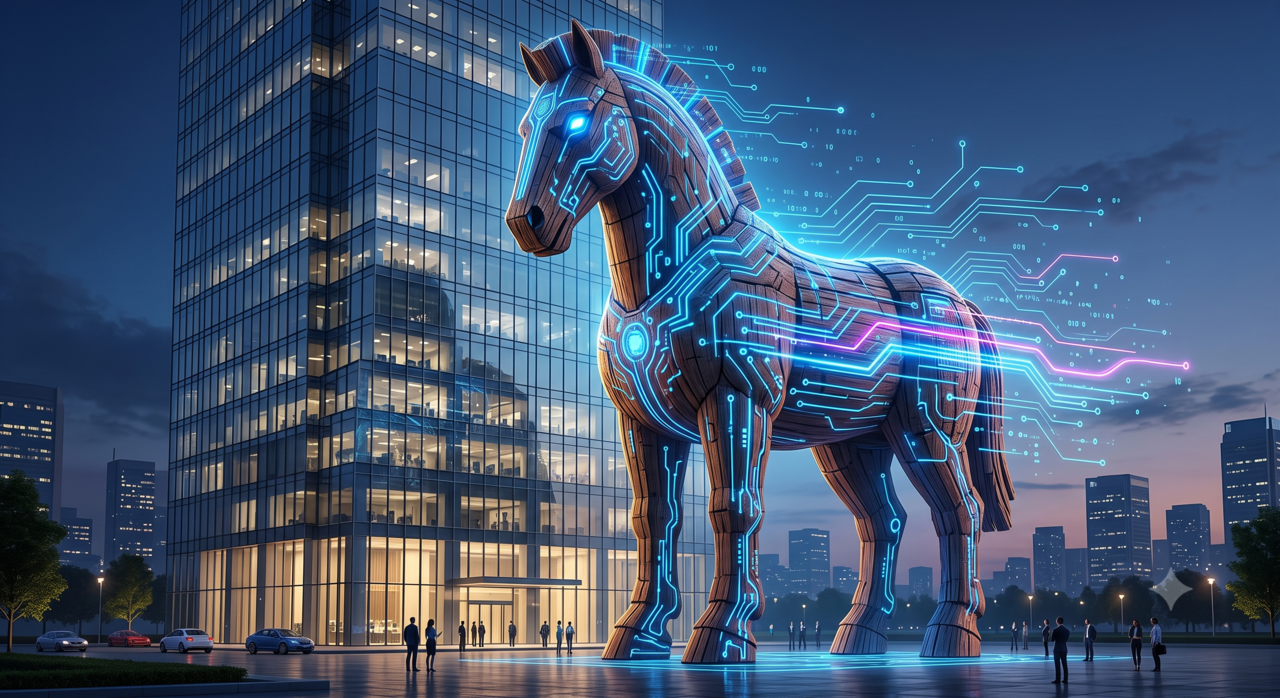
Key Summary
- The second installment of Professor Kim Jeong-deok’s special series, covering the core theme of Part 1, ‘hacking perspectives’
- Companies pour massive capital into firewalls and multiple layers of advanced security solutions to defend their cyber territory, a period the author calls ‘the era of the most formidable digital walls in history’
- As technical defenses grow stronger, major security breach incidents paradoxically continue to occur, and the cause lies not in technology but in ‘human psychology and cognitive biases’
Analysis
Cognitive bias brings systems down more often than the most expensive piece of security equipment. In 2024 alone, more than 70% of security breach incidents worldwide began with human error or social engineering. Episode 2 of ‘Hacking Security,’ serialized on Boan News, tackles this point head-on. The stronger the technology gets, the more the human becomes the entry point.
The Trojan Horse and the Lesson of Cognitive Bias
The Trojan Horse story began after a ten-year siege, when the Greek forces left a giant wooden horse outside the city walls and withdrew. The Trojans brought the offering inside. Tradition tends to emphasize this far, but the more important question is why they brought it in without suspicion.
What fell here was not a physical fortress. What fell was the gods — that is, trust and loyalty, the reverence owed to a god and an object of worship. The attacker exploited not the city wall but the recipient’s trust structure. Three thousand years later, the structure is the same. Email attachments, phone calls disguised as legitimate contacts, and ransomware masquerading as a trusted tool are all Trojan Horses in the form of an ‘offering.’
What the author highlights in this example is not the sophistication of the attack. It is the recipient’s decision, rationalized within their own belief system. What stopped the doubt was not technology but perspective.
Socratic Questions: Conversational Attacks That Target Cognitive Bias
Socrates kept asking his students endless questions. He never gave answers; instead, he let the other person recognize the logical gaps in their own replies. This dialectic method is a core technique of classical philosophy.
Yet the same structure is the archetype of social engineering. Attackers stimulate a target’s cognitive bias with questions like ‘Have you ever experienced something like this?’ The user, driven by a desire to help or by deference to authority, hands over information voluntarily. That information is often an account, a card number, or access credentials to an internal system.
Here is a concrete example. In an attack on a call center employee, the question ‘May I ask you a few questions to verify the customer’s identity?’ is indistinguishable from a normal work process. At the end of that question sits a password. From a practitioner’s perspective, this pattern works more precisely than signature-based detection.
Hacking Perspectives: The Layer Technology Cannot Reach
Professor Kim Jeong-deok’s ‘hacking perspectives’ pinpoints this exact issue. Attackers don’t break the code — they change the person’s perspective. This is not a problem of cryptographic algorithms or firewall rules.
What companies spend on defending their cyber territory grows every year. Despite that, major breach incidents never stop. In an era when even Claude AI accounts are being stolen through infostealers, technology alone cannot provide the answer. This is an era of ‘the most formidable digital walls in history’ and, at the same time, the era in which the most breaches are being recorded. Within it, the cognitive bias of the human resident remains the weakest link.
Why Human Security Must Be Redesigned in the AI Era
Generative AI crafts convincing phishing emails in seconds. There are no grammatical errors. It references the target’s job title, department, and recent projects. The speed at which cognitive biases become a target operates on a completely different scale from the past.
That said, AI is also part of the solution. Behavior-based anomaly detection, user behavior analytics, and short micro-trainings at the moment of decision can supplement human cognition. Yet technology cannot replace cognitive bias. It is only an auxiliary tool.
What to Do Right Now
- Hold links in emails and messages from unclear sources for 24 hours, then reconsider whether to click.
- Establish a team rule that ‘urgent’ requests from someone in authority must be verified once more through a separate channel (phone, in person).
- If you are asked for identity verification or payment information, hang up on any channel and call back through the official main number.
- Run a team-wide phishing simulation once a month, and share click-through rates and reporting rates as KPIs.
- Place a note by your desk that says, ‘If someone asks for it, I do not give it.’
Key Issues at a Glance
Responding to perspective hacking starts with culture design, not tool adoption. The Trojan Horse recipient did not fail to know the danger — it was a belief system that did not question the offering’s identity that allowed the infiltration to pass. The same structure operates today at the very front line of decisions: internal rules, payment approval procedures, and trust placed in external contacts.
- The 10-second rule before deciding: For every external request, ask yourself, ‘Can I push this decision back by 10 seconds?’
- Role-based permission redesign: Structure access so that two or more people must approve before the same information is exposed, reducing individual bias.
- Cognitive bias branch training: Train with cases around three biases — confirmation bias, authority bias, and urgency bias.
Frequently Asked Questions
You say cognitive bias is the biggest vulnerability in cybersecurity — is the human problem really larger than the technology problem?
Industry statistics for 2024 show that more than 70% of major breach incidents began with human error or social engineering. That is higher than the proportion of technical flaws. Attacks that bypass human cognition also slip past signature-based detection more easily.
Does the Trojan Horse example still apply to security today?
The form is different, but the essence is the same. Attachments, phone calls disguised as legitimate contacts, and ransomware masquerading as a trusted tool are all Trojan Horses in the form of an offering. The structure of attacking the recipient’s trust is no different from 3,000 years ago.
AI has made social engineering more sophisticated — how should an ordinary office worker prepare?
Shifting your default stance from ‘trust’ to ‘verify’ is the starting point. Assume that any request for identity verification, payment, or a password is fraudulent by default, and confirm through an official channel. That habit alone reduces significant risk.
What does the Socratic method have to do with attack techniques?
Socrates used questions to let the other person recognize their own logical gaps. Attackers use the same structure to stimulate the target’s psychological gaps and induce voluntary information disclosure. It is the archetype of conversational design that creates cognitive bias.
Ultimately, the strongest line of defense is not in the code. It lies in the user’s awareness and judgment. What the Trojan Horse demonstrated, and what the Socratic method has repeated for more than 2,400 years, is that the human mind is both the most sophisticated channel and the most decisive vulnerability. Advanced security solutions must be redesigned from the starting point of acknowledging this fact. Cognitive bias is a weakness, but once recognized, it becomes the most powerful first line of defense.
Expert Commentary (AI)
Information Security Specialist
The diagnosis that ‘humans are the weakest link’ is industry orthodoxy, but the real challenge is designing verification defaults that hold up even when people make mistakes, not individual vigilance
The diagnosis that most breach incidents originate in human factors aligns with major industry statistics such as the Verizon DBIR, and the direction is valid as a check on the practice of pouring budgets into firewalls and solutions alone. Suggestions such as verification through a separate channel, two-person approval structures, and decision-delay devices are controls whose effectiveness has been proven in practice and align with zero trust’s ‘verify, then trust’ principle. However, the frame of ‘humans as the weakness’ easily translates into a culture of blaming users, and research has documented the side effect that this lowers incident-reporting rates and actually delays initial response. Using phishing-simulation click rates as KPIs also tends to invite metric gaming and employee pushback, and accumulated research confirms the time-decay problem of training effectiveness. As a complement, technical safety nets that make human error non-fatal are essential alongside: email authentication such as DMARC, phishing-resistant authentication (passkeys), and withdrawal delays and limits. The industry outlook is that as generative AI raises the difficulty of impersonation, security awareness training must move beyond a one-off session toward an ongoing operational system of human risk management.
Behavioral Science & Cognitive Bias Researcher
Treating cognitive bias at the moment of decision as an attack surface is theoretically sophisticated, but the gap between knowing a bias and resisting it is the biggest weakness of this topic
The view that authority bias, urgency bias, and confirmation bias serve as infiltration paths for social engineering aligns with the dual-process theory of Systems 1 and 2, and the insight that attacks target the heuristics of the decision moment rather than logic is accurate. A decision-delay device like the ’10-second rule’ is a simple nudge that forces System 2 to engage, and it connects to the way its effects have been reported in pre-commitment studies. However, the evidence that knowledge of bias translates into actual resistance behavior consistently appears weakly in meta-analyses of bias training, and the limited effect of one-off case training is a structural limitation of this topic. Considering the evidence that environmental redesign — such as default changes and approval workflow enforcement — has a larger effect size than individual training, ‘culture design’ must be translated into concrete procedural changes or it will not translate into substantive defense. The analogy between the Socratic method and phishing dialogue is rhetorically attractive, but it is worth noting that the psychological mechanisms are actually opposite: the former induces reflection, while the latter stimulates heuristics. In the AI era, the success of defense will be determined not by a speed race with threats but by the habituation of verification procedures and whether they are embedded in the environment.
Critical Analyst
Behind the narrative of ‘the era of the most formidable digital walls’ lies a structure in which the human security market and the book/serialization ecosystem profit
On the surface, it reads like a deep insight pointing out the limits of technology investment, but if you first ask cui bono, the picture changes. ‘Humans are the weakest link’ is an orthodoxy repeated for more than 20 years, and the reason this orthodoxy is renewed with each cycle may well be that the markets for security awareness training, phishing simulations, and human risk management platforms are sold on top of this very narrative. The structure in which the serialization starts from a summary of a specific professor’s Part 1 and links to a news serialization and external blogs reads as a funnel that draws readers toward the book and follow-up content. The timing of generative-AI phishing fear also aligns precisely with the message that ‘now is the time to spend money on people and culture,’ steering in a direction that fuels demand for education vendors and consulting. That the click-rate and reporting-rate KPIs that appear in the action guide are also the dashboard metrics of phishing simulation products is hard to read as coincidence. What we should really pay attention to is the fact that the orthodoxy of cognitive bias is being distributed on top of a stakeholder map of ‘who sells that training and tool, and who pays the money,’ and readers need to think for themselves about whose revenue this formidable-wall narrative ultimately justifies.
Underlying Scenarios
- Funnel hypothesis of serialization-book-lecture pipeline: Given that the article openly states it is a ‘core theme of Part 1 of the book’ and links to a Boan News serialization and external blogs, this piece may not be independent analysis but content marketing aimed at book promotion and follow-up paid content (lectures, consulting) demand generation.
- Vendor demand-creation hypothesis: The emphasis on generative-AI phishing threats and the recommendation of ‘monthly phishing simulations with click-rate and reporting-rate KPIs’ overlapping in timing is, circumstantially, a message aligned with industry stakeholders whose growth narrative benefits from the human risk management solutions and security awareness training markets.
Leave a Reply