
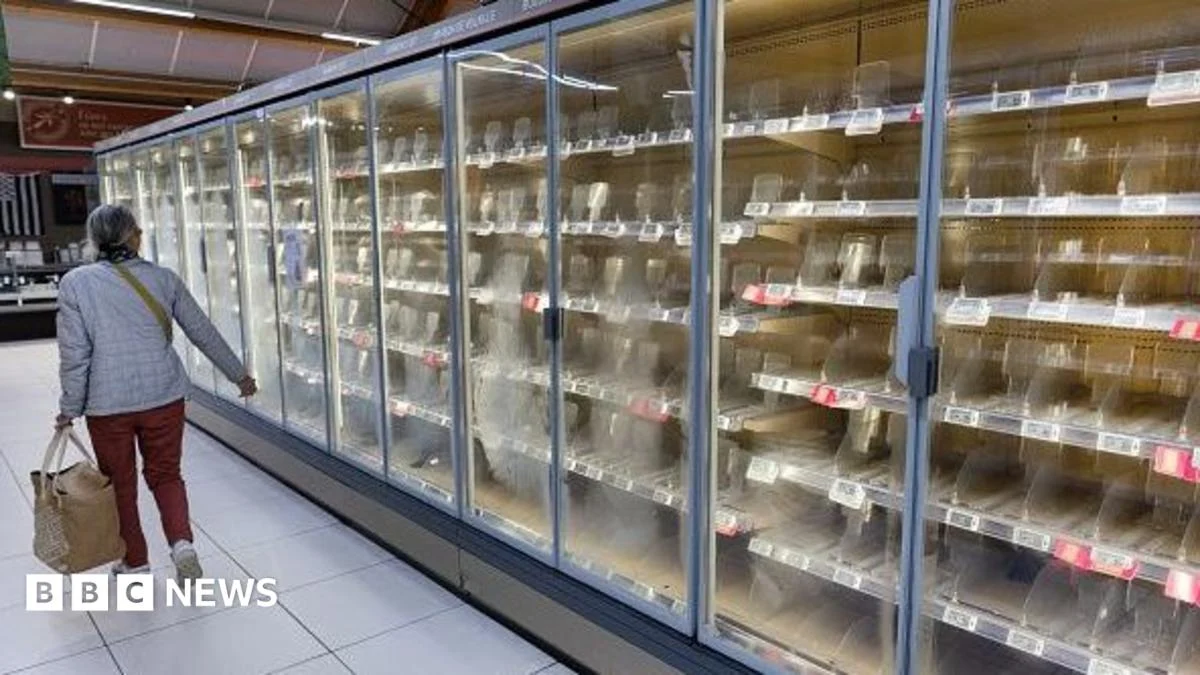
As suspicious cyberattacks targeting refrigerators and freezers have affected several European supermarkets, the security vulnerabilities of internet-connected appliances and industrial equipment have become central to a major debate. Following this incident, discussions have called for a thorough qualitative safety review to determine whether everyday devices such as humidifiers, heaters, and washing machines share the same risks as vehicles and energy infrastructure. However, a device does not become immediately hackable simply because it is connected to the internet, and major manufacturers have also invested significant resources in security.
Connected-Device Attack Surface Revealed by Freezer Attack
Smart devices connected to the internet offer convenience and operational efficiency through remote control, but they can also become targets for abuse by malicious actors. Security researchers demonstrated in 2015 that vulnerabilities in a Samsung smart refrigerator could be exploited to intercept internet traffic, illustrating that real-world exploitation may also be possible with consumer appliances. However, there is still no confirmed evidence that the appliances themselves were targeted in the November attack against European supermarkets.
The UK’s National Cyber Security Centre (NCSC) is working with international partners and industry collaborators to understand the incident in advance, but it has not identified any impact in the United Kingdom. Researchers found that more than 800 refrigeration and building-control interfaces connected to UK retailers were accessible over the public internet. While public accessibility does not necessarily mean the systems can be hacked, the warning is that weak passwords or software vulnerabilities could leave them exposed as an attack surface if exploited.
Boundaries of Equipment Ownership and Repair Responsibility
The central issue is where responsibility for equipment security should lie. SentinelOne researcher Tom Hegel said retailers need to clarify who owns the security of the relevant equipment, rather than merely identifying the organization responsible for repairs. As connectivity provides convenience, security must keep pace, and a warning cautioned that if attackers seize legitimate control functions, even ordinary functions such as defrosting could be turned into a tool for disruption. Assessments also concluded that configuration changes could cause physical damage to actual inventory, beyond simply disrupting computer systems.
Retailers in the UK have previously held security discussions with the government and major food distributors about cyber resilience in preparation for incidents. Helen Dickinson of the British Retail Consortium emphasized that cyber incidents are a major concern for retailers and that companies are sharing information and strengthening their defenses with the NCSC. After M&S and Co-op were targeted by ransomware attacks in May 2025, fresh deliveries ran short on some shelves, prompting customers to voice dissatisfaction with empty shelves.
Infrastructure Risks Spreading Beyond the Home
Outside the home, connected technologies are used to remotely manage industrial machinery and vehicles, while equipment at power plants and in water-supply chains is also monitored through mobile connectivity. Security expert Ken Munro cited a 2015 demonstration in which researchers remotely hacked a Jeep through an internet-connected entertainment system, saying the incident led to improvements in vehicle security. He assessed that connected security at UK utility companies was generally sound, but that global standards vary.
Small, cash-strapped utility companies that may depend on older and vulnerable equipment were identified as the greatest source of concern. Olivier Daloy, a cybersecurity expert at Zscaler, said that without adequate protection, every internet-connected factory and piece of equipment could face similar risks, extending from automobile manufacturing to power and transport infrastructure. This goes beyond inconvenience or information leakage from appliances and demonstrates the possibility that a loss of control could result in physical harm.
Security Standards and Consumer Responses
UK law has required manufacturers of some consumer smart devices to meet minimum cybersecurity standards, including passwords and security updates, since April 2024. Former NCSC chief executive Ciaran Martin noted that there is much to demand of big technology companies to create safer devices and products, and recommended that consumers update their devices and enable multifactor authentication (MFA) where possible. He said that enabling multifactor authentication takes only a few seconds but can still be inconvenient, illustrating the practical barrier that security convenience poses to widespread adoption.
This incident shows that connected-device cybersecurity must be treated as an essential requirement at the design stage rather than an optional added feature. Manufacturers should go beyond merely meeting minimum security standards and clearly define responsibility for equipment, update periods, and remote-control access. Retailers should check that refrigeration and building-control interfaces are not unnecessarily exposed to the public internet, while consumers should make updating older devices and configuring authentication part of their everyday security habits. Further reporting is needed to establish the technical scope of the attack and where responsibility lies.
Source
This article was prepared with reference to the following source: BBC Tech — If hackers can take control of a supermarket freezer, how vulnerable is other tech?
Leave a Reply